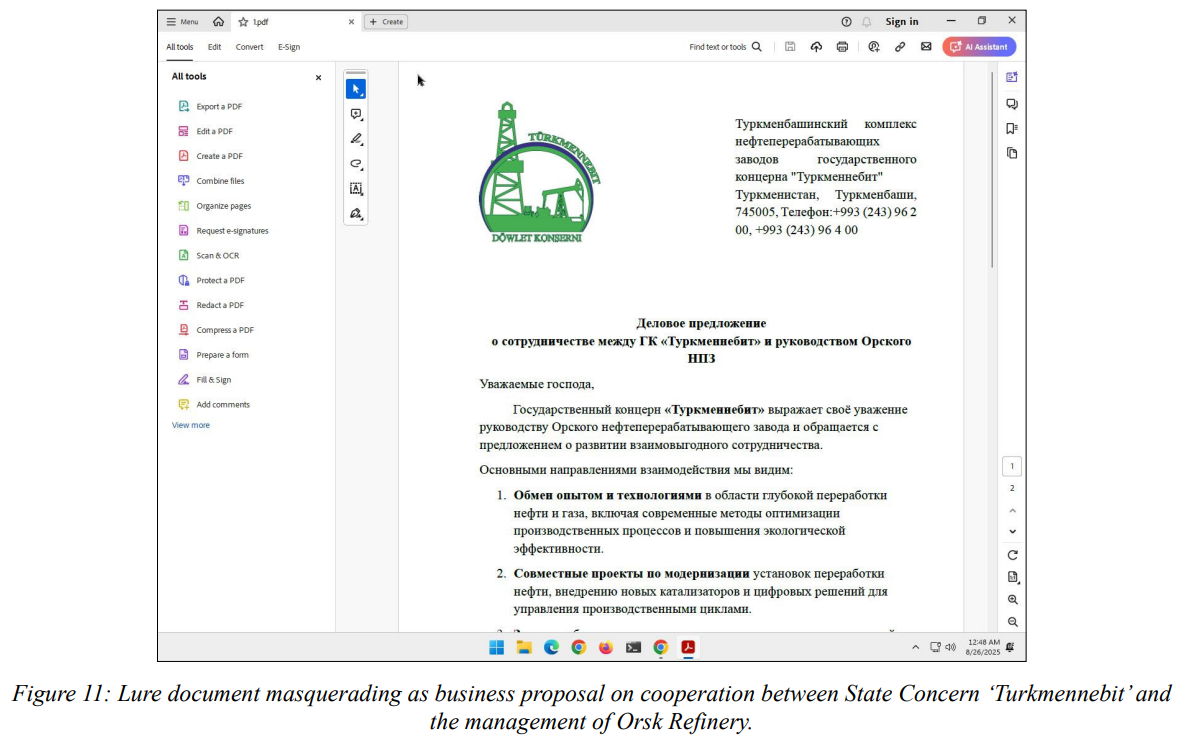
SILENT Lynx, a threat actor believed to be based in Kazakhstan, has been observed conducting espionage campaigns against energy and government targets across Central Asia, including an assault on the Orsk Oil Refinery in southern Russia and the government of Nizhny Novgorod.
Researchers from Cisco Talos and Recorded Future describe Silent Lynx (also tracked as UAT-6275 and TAG-193) as a persistent actor with a track record of targeting ministries, diplomatic missions and civil society organisations since at least 2024, using spear‑phishing via compromised government email accounts and staging malware through trusted public services such as GitHub to boost credibility. The group’s operations overlap with previously documented clusters such as YoroTrooper, ShadowSilk and Hydra Saiga.
The toolkit is deliberately lightweight, consisting of PowerShell reverse shells, custom shells in C++, C#, and Go, commodity tunnelling tools and spear‑phishing emails sent via compromised government accounts in Tajikistan and Kyrgyzstan. Staging platforms include GitHub, Telegram and hijacked legitimate servers.
The researchers highlight several concrete indicators: open live directories on public servers with payloads, keyboard input shown in Latin with a Russian layout, and GitHub commits aligned with Astana working hours. Two malware samples were uploaded to VirusTotal from Kazakhstan within minutes of compilation, and ProtonVPN egress IPs geolocated to Kazakhstan were observed accessing Silent Lynx infrastructure.
In April 2026, Silent Lynx began using an exploit for the first time to deliver malware, abusing CVE-2025-8088 to place files in the Windows Startup folder, and researchers note growing interest in Linux as the group expands its toolset. Full joint research with IOCs is available in the Virus Bulletin paper.