News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Fri 23 Oct· 6 articles
-
Attackers Exploit PHP2Shell Faster Than Organisations Can Patch It
New data shows that organisations aren’t patching PHP2Shell as quickly as attackers are exploiting it. The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, were publicly disclosed on 21 October, and threat activity surged immediately. Cloudflare’s…
-
Mirai Botnet Tries to Exploit PHP2Shell, but Finds No Way In
Researchers have linked attempts to exploit PHP2Shell to a Mirai-derived botnet, with new ASLR-bypass exploits emerging, though no confirmed in‑the‑wild compromise has yet been demonstrated. Two days after PHP issued emergency fixes for the PHP2Shell flaws,…
-
PHP Warns of Unpatched RCE Risk in Rare Session Configurations
PHP has warned of a fresh, unpatched RCE pathway on web servers, just two days after it released emergency fixes for the PHP2Shell flaws. The new issue, tracked as CVE-2026-115560, affects only web applications that are configured in a narrow, unusual way…
-
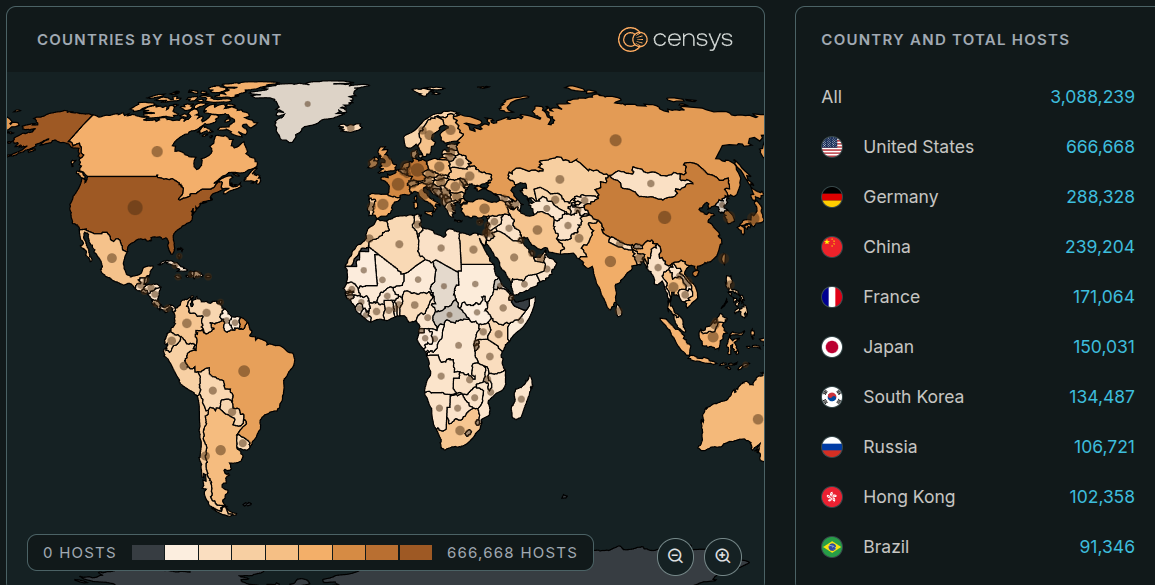
Critical PHP Flaws Trigger Millions of Exploit Attempts in Days
PHP2Shell has prompted a surge of activity after two critical PHP core vulnerabilities were disclosed, tracked as CVE-2026-109618 and CVE-2026-109619, with a CVSS of 9.2. The issues reside in the PHP engine itself and allow unauthenticated remote code…
-
Attackers exploit PHP2Shell flaws to build a Mirai derived botnet
Threat researchers warn that attackers are probing PHP2Shell vulnerabilities (CVE-2026-109618 and CVE-2026-109619; CVSS 9.2) to drive infected hosts into a Mirai-derived botnet variant named Potassium. The exploits revolve around unauthenticated remote code…
-
Okta fixes critical Access Gateway flaws enabling remote code execution
Okta has released security advisories for four vulnerabilities in Okta Access Gateway (OAG), disclosed on 22 October 2026. The flaws span PHP runtime components (PHP2Shell) and the Admin Console, with the most severe being a command-execution bug rated…
Thu 22 Oct· 9 articles
-
PHP Flaw Disclosures Trigger Widespread Scanning, but Not Confirmed Breaches
Darktrace reports that the October 2026 disclosures of CVE-2026-109618 and CVE-2026-109619, both allowing unauthenticated remote code execution in PHP contexts, prompted widespread scanning of internet-facing PHP deployments. Public guidance emphasised…
-
Exposed PHP2Shell tooling targets PHP 8.4, but no sites were vulnerable
SOCRadar Threat Intelligence Unit researchers found PHP2Shell exploit tooling on an attacker-controlled server whose working directory was exposed via an open, unauthenticated directory listing. The central asset is a lab-tested PHP2Shell remote code…
-
AWS Saw PHP2Shell Attacks Before Two Critical PHP Flaws Were Disclosed
AWS Threat Intelligence detected PHP2Shell exploitation attempts four days before public disclosure of the two critical PHP flaws tracked as CVE-2026-109618 and CVE-2026-109619. The earliest activity, dating to 17 October 2026, appeared in MadPot telemetry…

-
Gcore Offers Free Web Protection to Governments After PHP Attacks
Gcore has announced that its WAAP Enterprise plan will be free for public agencies and government bodies until 31 December 2026. The move follows the php2shell vulnerabilities that disrupted public websites across Europe earlier in the week. Gcore states…
-
Attackers Target Critical PHP Flaws Before Patches Were Released
SecurityWeek reports a coordinated industry and government response to two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, which allow unauthenticated remote code execution. The bugs were identified by Wiz, OpenAI and Calif in August, with PHP…
-
cPanel Patches Actively Exploited PHP Flaws Threatening Shared Hosting
Cpanel has released security updates addressing two PHP2Shell flaws and a WP Toolkit bug that affect shared hosting environments. The patches cover three CVEs: CVE-2026-109618 and CVE-2026-109619 in PHP, and CVE-2026-107663 in WP Toolkit. The PHP fixes are…
-
QNAP Warns of Active PHP Flaws as Device Patches Remain Unavailable
QNAP has warned that two PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, in PHP itself threaten QTS, QuTS hero, QuTScloud and several QNAP apps. The flaws permit unauthenticated, remote code execution, with exploitation attempts already observed in…
-
Over a Million PHP Systems Face Exploitation After RCE Flaws Go Public
Security researchers tracked a rapid surge of exploitation activity targeting two critical PHP RCE flaws, now tracked as CVE-2026-109618 and CVE-2026-109619, with patches released on 21 October after an embargo and weeks of coordinated disclosure. Initial…
-
Amazon Detects PHP2Shell Exploit Attempts Targeting Its Honeypot
Amazon’s Threat Intelligence team detected an attempt to exploit the newly disclosed PHP2Shell vulnerabilities on 17 October 2026, targeting its MadPot honeypot service. The activity originated from an IP address tied to a commercial anonymisation service…
Wed 21 Oct· 16 articles
-
Critical PHP Flaws Enable Unauthenticated Code Execution on Servers
Two critical PHP flaws, dubbed “php2shell”, could let unauthenticated attackers run code on affected web servers. CVE-2026-109618 enables remote code execution through out-of-memory corruption, while CVE-2026-109619 involves stale global state. The bugs were…
-
PHP Patches PHP2Shell Flaws After Attack Attempts Target Servers
PHP has issued patches for two critical vulnerabilities, named PHP2Shell, which can yield unauthenticated remote code execution (RCE) on web servers running PHP. The flaws are tracked as CVE-2026-109618 (out-of-memory corruption) and CVE-2026-109619 (stale…
-
Critical PHP Flaws Trigger Emergency Patches as Attacks Begin
A security advisory surrounding two critical PHP vulnerabilities, tracked as CVE-2026-109618 and CVE-2026-109619, prompted widespread maintenance and emergency updates across websites on 21 October 2026. The flaws could allow an attacker to run malicious…
-
PHP Zero Days Put Millions of Websites at Risk of Remote Takeover
Two critical PHP zero-days are driving widespread disruption as experts warn that nearly 70% of websites require core software updates to fix the flaws. The vulnerabilities affect PHP itself and enable remote code execution, potentially allowing attackers to…
-
Critical PHP Flaws Enable Remote Code Execution Without Login
PHP released fixes on 21 October 2026 for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, each rated 9.2 on CVSSv4. Both can enable unauthenticated remote code execution with the privileges of the web worker. The flaws affect PHP…
-
Critical PHP flaws enable unauthenticated remote code execution across versions 5 to 8
On 20 October 2026, the PHP security team issued a preliminary notice about two critical remote‑code‑execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on the CVSS scale. Patches were released on 21 October 2026 at 14:00 UTC after…
-
Critical PHP flaws enable remote code execution as exploit PoCs emerge
SANS ISC reports a critical PHP vulnerability affecting the PHP core, tracked as CVE-2026-109618 and CVE-2026-109619. PHP[.]net announced a critical update and the information ConIns notes that the information level has been raised to YELLOW due to the…

-
PHP Fixes Two Critical Flaws That Could Let Attackers Run Code
On 21 October 2026, the PHP team released updates to fix two critical, unauthenticated remote code execution flaws: CVE-2026-109618 and CVE-2026-109619, both rated 9.2 under CVSS v4. The vulnerabilities affect PHP 8.2 versions before 8.2.35, 8.3 before…
-
PHP Patches Critical Unauthenticated Flaws That Expose Web Servers
PHP has issued emergency patches for two critical PHP2Shell remote code execution flaws that allow an attacker to run code on a web server without an account. The fixes are included in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, and the PHP team cautions that…
-
Critical PHP Flaws Enable Remote Code Execution Across Web Servers
Unit 42 reports two critical remote code execution vulnerabilities in PHP: CVE-2026-109618 and CVE-2026-109619, both rated 9.2 on CVSS 4.0. CVE-2026-109618 arises from handling out-of-memory errors via longjmp(), which leaves request memory uninitialised due…
-
PHP2Shell Flaws Put PHP Servers at Risk of Remote Code Execution
Two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, have been named PHP2Shell. The PHP security team rated both 9.2 on CVSS v4.0, and researchers say they could allow remote code execution. The flaws were leaked on 20 October 2026, two…
-
PHP2Shell flaws threaten remote code execution across PHP websites
Two critical PHP remote code execution flaws, CVE-2026-109618 and CVE-2026-109619, were disclosed ahead of the security patches scheduled for 21 October 2026. Together dubbed “PHP2Shell”, the vulnerabilities were due to be announced at 2pm GMT alongside…
-
NCSC urges PHP users to patch flaws that could enable server takeover
The UK National Cyber Security Centre (NCSC) is urging organisations to act on two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619. PHP has issued a security update fixing the flaws, which affect PHP installations across versions. Under…

-
Critical PHP2Shell flaws could expose servers to remote code execution
Details of two critical PHP vulnerabilities, dubbed PHP2Shell, have leaked online before the planned coordinated disclosure and release of fixes. Tracked as CVE-2026-109618 and CVE-2026-109619, both have a CVSS score of 9.2 and could allow remote code…
-
PHP Prepares Emergency Fixes for Two Critical RCE Flaws
PHP has issued an out-of-cycle security release addressing two critical PHP RCE flaws, collectively nicknamed php2shell, with a CVSS v4.0 score of 9.2. The vulnerabilities are identified in the leak as CVE-2026-109618 and CVE-2026-109619. Researchers from…
-
PHP Warns of Critical Flaws That Could Expose 1.3 Million Hosts
PHP maintainers warned that two critical vulnerabilities, rated 9.2 out of 10, are expected to be patched imminently. In an advisory published on 20 October 2026, they urged all PHP users to prepare to upgrade as soon as the releases are available, while…
Tue 20 Oct· 1 article
-
PHP Prepares Critical RCE Fixes as Leaked Flaws Raise Alarm
PHP announced a security release for 21 October 2026 at 14:00 UTC to address two critical flaws, CVE-2026-109618 and CVE-2026-109619. The article says leaks describe them as remote code execution vulnerabilities and rate them CVSS v4.0 9.2. PHP’s advance…
No older articles match these filters.