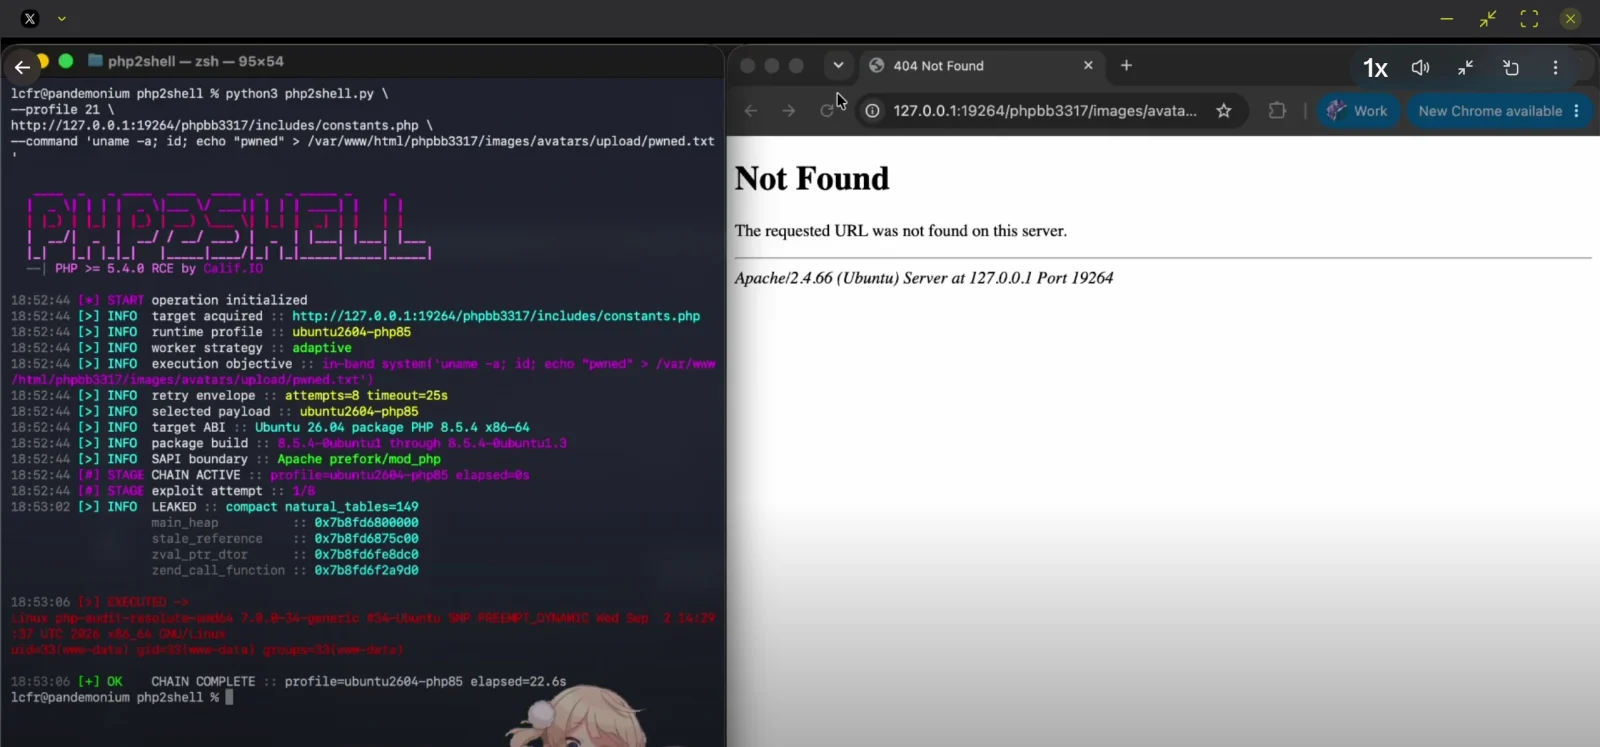
PHP announced a security release for 21 October 2026 at 14:00 UTC to address two critical flaws, CVE-2026-109618 and CVE-2026-109619. The article says leaks describe them as remote code execution vulnerabilities and rate them CVSS v4.0 9.2. PHP’s advance notice did not confirm the flaw types or name affected and fixed versions; the project said those details would be published with the release.
The warning followed an anonymous Hacker News post on 20 October claiming two PHP flaws had a CVSS score of 10.0. Kevin Beaumont said the CVE details had been leaked before a patch was available, and watchTowr said the flaws were real. However, no exploitation in the wild or public proof-of-concept had been confirmed. Claims that every PHP release from version 5 onwards is affected remain unverified.
PHP is widely used by platforms including WordPress, Drupal and Magento. The article cites an estimate of about 1.5 million internet-facing hosts reporting a PHP version, with 59% running PHP 8.1 or older, which no longer receive official fixes. Administrators are advised to inventory PHP applications and versions, install the fixed releases as soon as they are published, and plan upgrades from unsupported branches. The article also suggests considering isolation of internet-facing PHP applications until they can be patched.