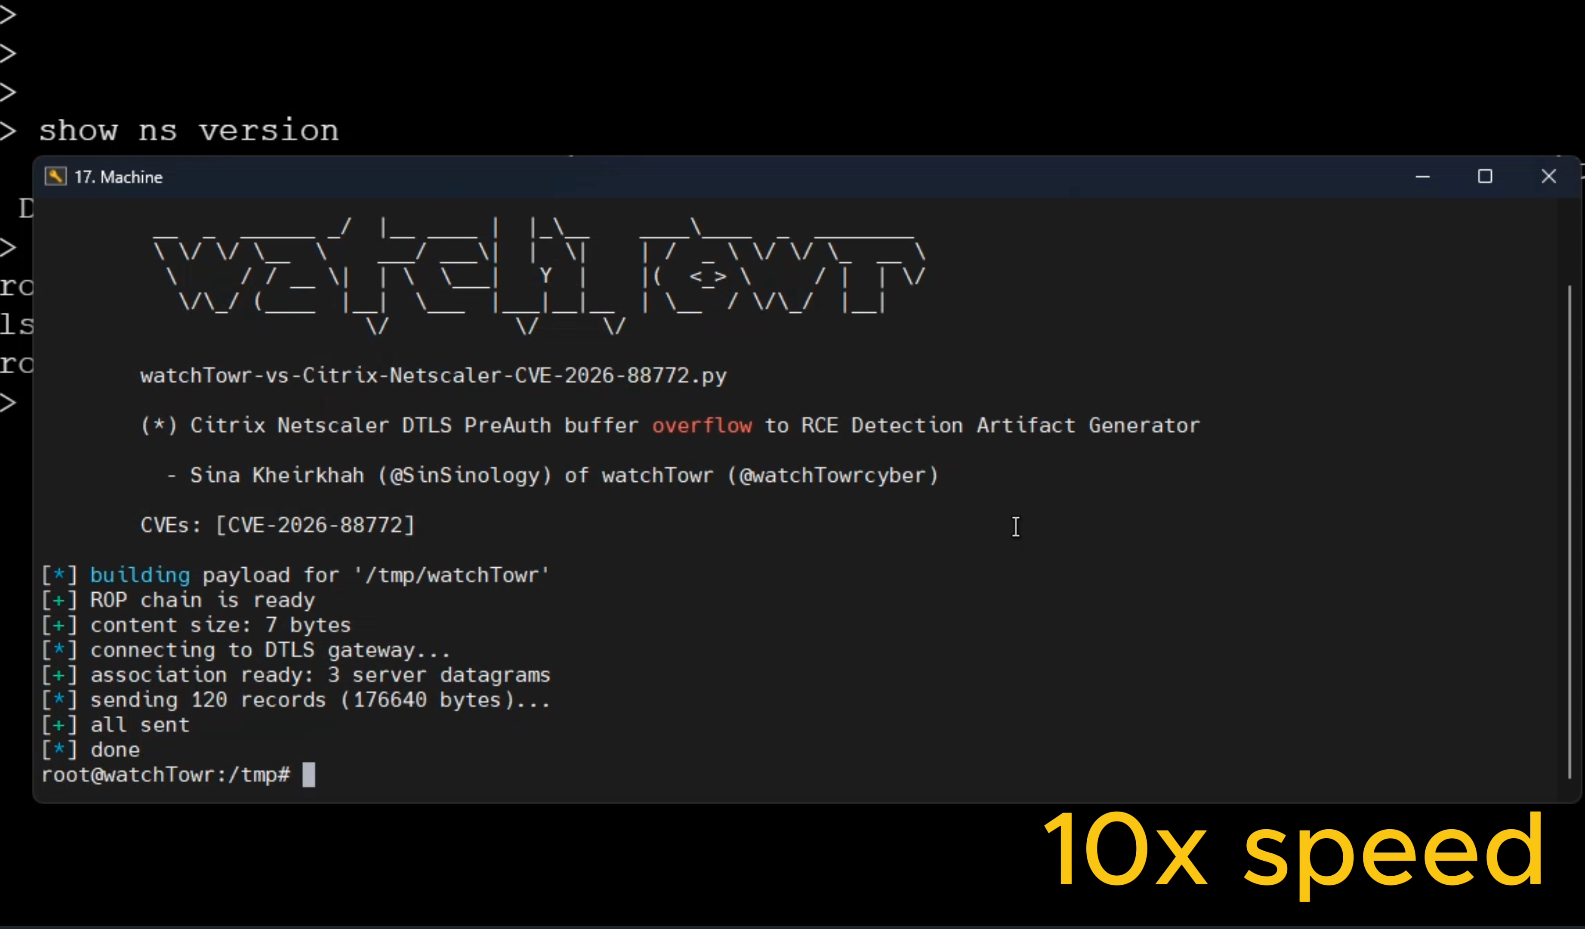
CITRIX NetScaler ADC and Gateway were found to be vulnerable to a pre-authentication memory overflow, tracked as CVE-2026-88772, with a companion flaw CVE-2026-88771 also exploitable in the wild. The issues were actively exploited as a zero‑day, leading CISA to add both CVEs to its Known Exploited Vulnerabilities catalog on 27 September 2026. Public technical details and a working PoC were subsequently released by watchTowr, heightening risk for unpatched devices. The combined impact is severe, with a CVSSv4 score of 9.5 and the worst‑case outcomes including remote code execution or denial of service.
The root cause lies in how NetScaler reassembles DTLS handshake fragments. DTLS runs TLS over UDP, and a sequence of fragments can be copied into a small fixed buffer without proper size checks. An attacker, after completing the standard DTLS cookie exchange, can send crafted fragments that cause the reassembled message to exceed the buffer, corrupt memory and potentially execute arbitrary code.
The attack requires no authentication beyond reachability to the device, which is why exposure at the network edge is particularly dangerous. Public uptake of the PoC confirms exploitation is occurring in practice.
Patching remains essential. Citrix lists fixed builds in bulletin CTX697096: NetScaler ADC and Gateway 14.1-73.37 and later, 13.1-64.23 and later, with corresponding FIPS versions, plus 13.1-NDcPP 13.1-37.279 and later. There is no full workaround for CVE-2026-88772; disabling DTLS can reduce exposure but CVE-88771 affects all deployments. After upgrading, organisations should review for signs of prior compromise.