News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Wed 9 Sep· 12 articles
-
HelmGuard Raises $7.3 Million to Expand AI Risk Platform in the US
HelmGuard, a UK-based startup focused on agentic governance, risk and compliance (GRC) and security, has raised $7.3 million in a seed round. The funding was co-led by Infinity Ventures and Frontline, with additional participation from FinTech Collective,…
SecurityWeek
-
Google Warns AI Is Giving Hackers Nation State Level Reach
Google’s Threat Intelligence Group (GTIG) warns that AI is increasingly enabling attackers with lesser resources to operate at “nation-state-level” reach. The piece describes a shift from basic prompt injection into enterprise AI systems to the development…
SecurityWeekUNC6508
-
Google Patches 180 Android Flaws, Including Critical Wi-Fi RCE
Google’s September 2026 Android security updates patch a total of 180 vulnerabilities across multiple components, with the rollout split into two patch levels. The first part, 2026-09-01, addresses 95 defects across Android runtime, Framework, System, Setup…
-
AMD, Arm and Nvidia Patch GPU Flaws Threatening Linux Systems
Chipmaker Patch Tuesday brought a trio of security advisories from AMD, Arm and Nvidia, detailing fixes for recently disclosed flaws across their graphics and compute products. AMD’s advisory addresses CVE-2026-43603, a NULL pointer dereference in the Linux…

-
Fortinet Patches Critical Flaws Enabling JWT Bypass and Traffic Hijacking
Fortinet has released patches for ten vulnerabilities across its product line, including two critical flaws. The most severe is CVE-2026-84390, a source-code information exposure affecting the FortiMonitorOnSight web portal. Fortinet says a remote,…
-
US agencies warn Chinese AI firms are distilling frontier models at scale
The NSA, CISA and FBI warn that Chinese AI firms are systematically “distilling” outputs from US frontier AI models to train their own systems. In a report cited by the agencies, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun and Z[.]AI are said to have…
SecurityWeek
-
Meta Unveils Muse AI Agent to Handle Users’ Everyday Tasks
Meta has rolled out Muse, a personal AI agent aimed at helping adults with day-to-day tasks such as scheduling, shopping, and long-term planning. The service is currently US-only and requires users to be 18 or older. Muse runs on a dedicated, secure virtual…
SecurityWeek -
ICS Patch Tuesday Fixes Critical Schneider, Siemens Flaws
Schneider Electric’s September 2026 Patch Tuesday advisory batch centres on its ICS portfolio, with four new advisories and updates to four others. The most critical flaw is an authentication vulnerability in the Modicon M580 and Modicon M580 Safety…
-
Ivanti Patches Critical Flaws Enabling Remote Code Execution
Ivanti has released security updates across three enterprise products—Neurons for ITSM, Sentry and Endpoint Manager Mobile (EPMM)—to address a set of critical and high-severity flaws. Neurons for ITSM accounts for the bulk of the fixes, with eight identified…
-
Novel Phishing Campaign Hides Malicious Pages Inside Victims’ Browsers
SecurityWeek reports a novel phishing campaign that defeats traditional page-based defences by rendering the malicious page inside the victim’s browser using blob URLs. The operation starts with a Docusign-themed email that includes a calendar invite to…
SecurityWeek
-
Proposed ORKS Standard Could Make Leaked API Keys Self-Destruct
A SecurityWeek piece by Matt Honea discusses a proposed open standard to make leaked API keys self-destruct within minutes rather than hours or days. The concept, dubbed ORKS (Open Revocable Key Standard), aims to give every API key a built‑in mechanism for…
SecurityWeek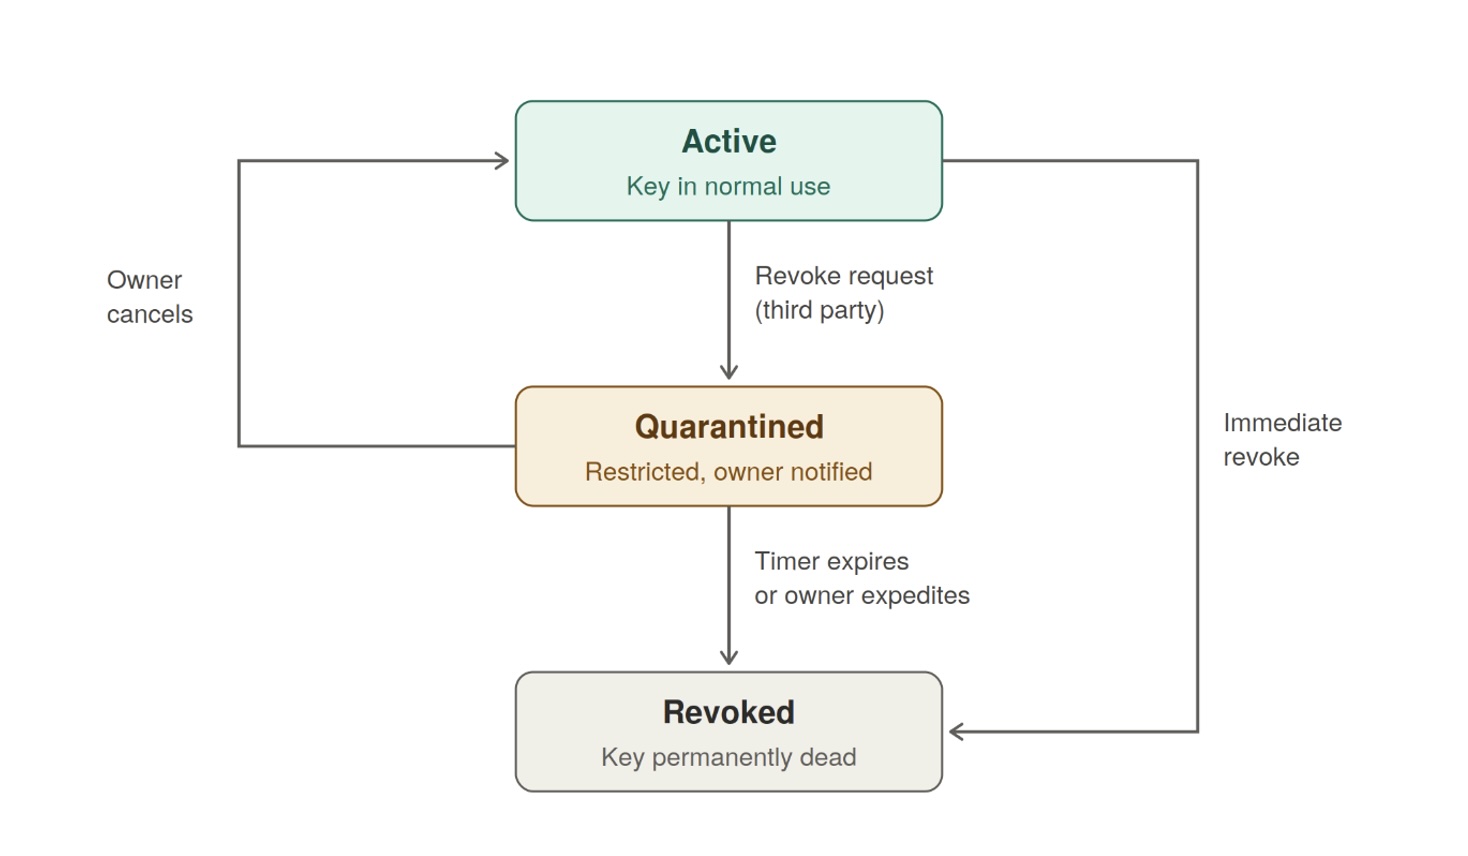
-
Google Fixes Exploited Chrome Zero Day Among 230 Flaws in Version 153
Google released Chrome 153 to the stable channel on 9 September 2026, delivering fixes for 230 vulnerabilities and notably addressing a zero-day that is already being exploited in the wild. The CVE tracked as CVE-2026-87491 is described as an out-of-bounds…