News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 8 so far |
Wed 9 Sep· 83 articles
-
Colorado School District Warns Cyberattack May Have Destroyed Files
A cyberattack forced Salida School District in Colorado to take its network offline on about 29 June, with the incident detected roughly two hours later. The district says the disruption damaged files stored on some devices’ hard drives and disrupted central…
DataBreaches -
Microsoft Maps Cloud App Attack Paths in New Threat Matrix
Microsoft has introduced the Cloud web applications threat matrix, a MITRE ATT&CK-aligned framework designed to help defenders understand, prioritise, and mitigate threats to cloud-hosted web apps and serverless platforms. The matrix maps techniques across…
Microsoft
-
AI Finds Thousands of Flaws, but Humans Patch Fewer Than 1%
A new analysis of public data from Anthropic’s Project Glasswing shows a widening gap between AI-generated vulnerability findings and those that actually reach disclosure or remediation. The Claude Mythos model produced 26,153 findings across various…
Dark Reading -
Google Chromium V83 articles this day · SecurityOnline first
BlueMoon Exploit Kit Races to Exploit Fresh Chrome and Windows Flaws · Chrome Zero-Day Chain BlueMoon Drops Espionage Backdoors on Windows
-
BlueMoon Exploit Kit Races to Exploit Fresh Chrome and Windows Flaws
Proofpoint reports that a chrome-and-windows exploit kit, dubbed BlueMoon, has been deployed rapidly by at least four groups after chaining three vulnerabilities to install malware of choice. The chain exploits two Chromium vulnerabilities in the V8 engine…
-
Chrome Zero-Day Chain BlueMoon Drops Espionage Backdoors on Windows
Four espionage-linked clusters are openly deploying a previously undocumented Chrome/Windows exploit chain, dubbed BlueMoon, within days of each other. The first attribution goes to APT31 (China-aligned) on 28 August 2026, with subsequent activity from other…
-
Chinese-Linked Spies Exploit Chrome and Windows Zero-Days
Proofpoint threat researchers have tracked a new BlueMoon exploit kit used in espionage campaigns, chaining Chrome/Chromium browser flaws with a Windows kernel privilege escalation to breach targeted networks. The operation, active from late August into…
-
-
US Agencies Warn Chinese AI Firms Stole Billions of Model Tokens
United States government agencies have alleged that several Chinese AI firms conducted “industrial-scale” distillation campaigns to extract and repurpose proprietary capabilities from leading US frontier models. In a joint advisory published on 8 September…
Dark Reading -
US Disrupts Xinbi Scam Marketplace and Freezes $52 Million
The U.S. Department of Justice has disrupted Xinbi Guarantee, an illicit Telegram‑marketplace for scam services, seizing control channels and freezing funds as part of its Scam Center Strike Force operations. In coordinated action, DoJ also drained two Xinbi…
The Hacker NewsXinbi Guarantee -
US Agencies Accuse Six Chinese AI Firms of Model Distillation
US federal agencies have published an advisory alleging that six Chinese AI firms have conducted industrial-scale extraction campaigns against US frontier models to accelerate their own development. The joint alert from the NSA, CISA and the FBI names…
Security Affairs
-
Attackers Scan Obsolete Proxmox VE 7 Servers for API Access
The ISC note reports that Proxmox has published an advisory about a vulnerability in older Proxmox VE versions, specifically affecting the Proxmox VE 7 line, which has not been supported for several years. According to the diary, the issue has drawn…
SANS ISC
-
Microsoft Exposes Passkey Bait Campaign Targeting Microsoft 365 Data
Microsoft Security Research outlines a multi-stage cloud intrusion campaign that begins with passkey-themed social engineering and culminates in identity compromise, persistence, reconnaissance, and targeted data exfiltration across Microsoft 365 workloads.…
Microsoft
-
HelmGuard Raises $7.3 Million to Expand AI Risk Platform in the US
HelmGuard, a UK-based startup focused on agentic governance, risk and compliance (GRC) and security, has raised $7.3 million in a seed round. The funding was co-led by Infinity Ventures and Frontline, with additional participation from FinTech Collective,…
SecurityWeek
-
Hackers Use Fake IT Calls to Hijack Microsoft 365 Accounts
Hackers are targeting senior Microsoft 365 accounts with highly tailored vishing campaigns that mimic internal IT helpdesk calls. The PREY-0058 operation, which aligns with UNC6671/BlackFile in some threat intelligence, starts with a phone call to executives…
SecurityOnlineUNC6671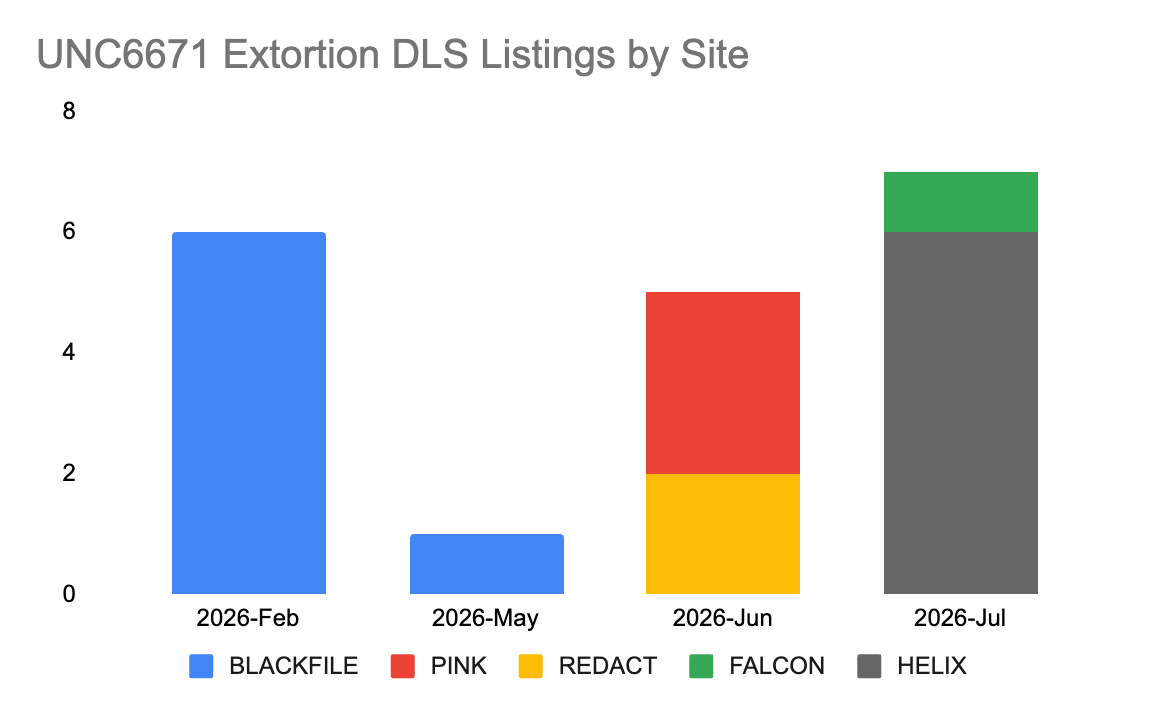
-
Palo Alto Firewalls Exposed to Root Code Execution Flaw in PAN-OS
On 9 September 2026, Palo Alto Networks disclosed a high-severity vulnerability in PAN-OS (CVE-2026-0310) that could allow unauthenticated remote attackers to execute arbitrary code with root privileges or cause a denial of service. The flaw resides in the…
-
Google Warns AI Is Giving Hackers Nation State Level Reach
Google’s Threat Intelligence Group (GTIG) warns that AI is increasingly enabling attackers with lesser resources to operate at “nation-state-level” reach. The piece describes a shift from basic prompt injection into enterprise AI systems to the development…
SecurityWeekUNC6508
-
Google Patches 180 Android Flaws, Including Critical Wi-Fi RCE
Google’s September 2026 Android security updates patch a total of 180 vulnerabilities across multiple components, with the rollout split into two patch levels. The first part, 2026-09-01, addresses 95 defects across Android runtime, Framework, System, Setup…
-
Cisco Warns Attackers Are Exploiting Critical FMC Flaws for Root Access
Cisco Talos researchers say two critical flaws in Cisco Secure Firewall Management Center (FMC) are being actively exploited in the wild. The vulnerabilities are CVE-2026-20079, an authentication bypass in the FMC web interface, and CVE-2026-20316, a flaw…
-
AMD, Arm and Nvidia Patch GPU Flaws Threatening Linux Systems
Chipmaker Patch Tuesday brought a trio of security advisories from AMD, Arm and Nvidia, detailing fixes for recently disclosed flaws across their graphics and compute products. AMD’s advisory addresses CVE-2026-43603, a NULL pointer dereference in the Linux…

-
GnuTLS CI Leak Exposed GitLab Token With Owner Access to 55 Projects
Truffle Security researchers detected a critical token leak tied to GnuTLS in June 2026, exposing a GitLab personal access token used by a public CI artifact. The token carried api scope and Owner privileges across 55 open‑source projects, including GnuTLS,…
SecurityOnline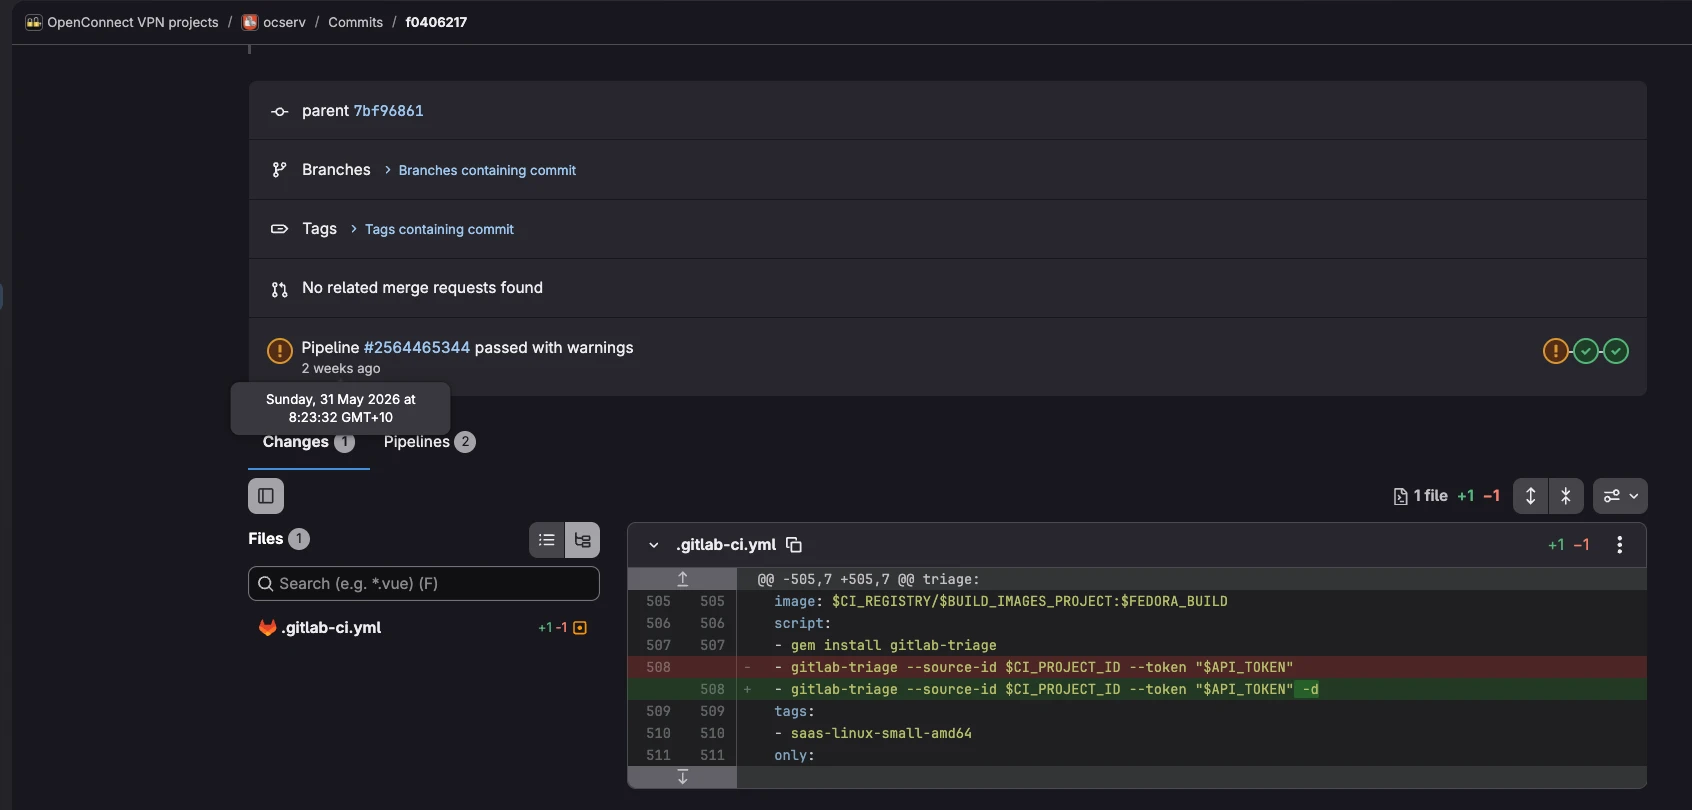
-
Credentialed Port Discovery Reveals Hidden Services Behind Firewalls
Credentialed pre-port discovery lets a scan engine skip outside-in probing and instead ask the host which ports it is listening on, provided the engine already has valid credentials for that host. Where a credential matches, the engine connects to the port…
Rapid7 -
Fake Shops Target 44,000 Brands in Vast DoppelCart Network
Researchers from Nebty have identified a vast network of fake online shops branded as “DoppelCart.” The cluster comprises almost 119,000 domains, with 118,787 of them using the .shop top‑level domain, amounting to about 2.72% of the .shop population they…
Malwarebytes
-
WeChat Zero Click Worm Can Hijack iPhones and Android Devices
A team of researchers at Calif, a Palo Alto-based cybersecurity startup, says it has built a tool capable of hacking Android and iPhone devices via a simple incoming call. The exploit, named WeWorm, hinges on a remote code execution (RCE) flaw in WeChat’s…
Infosecurity -
AI Workflows Let Attackers Hijack Privileged Actions Through Benign Requests
Security researchers have identified a new AI-driven attack flow dubbed “workflow identity hijacking,” which exploits an authorisation design flaw in modern enterprise AI pipelines. The gist is that threat actors can bypass standard security controls by…
Dark Reading -
Check Point Patches Critical VPN Flaws Enabling Remote Code Execution
Check Point has issued emergency security updates on 9 September 2026 to fix two critical VPN flaws in the Quantum Security Gateway line. The vulnerabilities, CVE-2026-85102 and CVE-2026-85103, are rated CVSS v3.1 at 9.8 (Critical) and could allow…
-
Fortinet Patches Critical Flaws Enabling JWT Bypass and Traffic Hijacking
Fortinet has released patches for ten vulnerabilities across its product line, including two critical flaws. The most severe is CVE-2026-84390, a source-code information exposure affecting the FortiMonitorOnSight web portal. Fortinet says a remote,…
-
Gigabud Trojan Hides Banking Fraud Inside Android Work Profiles
The Android banking trojan Gigabud has been enhanced to clone banking apps into a separate Android work profile, enabling fraudsters to dissociate a malware alert from subsequent transactions. Group-IB’s research, published on 9 September 2026, ties Gigabud…
InfosecurityGoldFactory -
Infostealer Logs Expose Thousands of Reusable AI Session Tokens
Threat researchers and identity security firms have warned that infostealer logs harvested from popular stealer families such as Lumma Stealer and Vidar contain a trove of credentials, session tokens and API keys that can be replayed to access AI services…
The Hacker NewsLumma Stealer -
Google Chrome4 articles this day · SecurityOnline first
Google Patches Chrome’s Seventh Zero Day of 2026 Under Attack · Google Fixes Exploited Chrome Zero Day Among 230 Flaws in Version 153
-
Google Patches Chrome’s Seventh Zero Day of 2026 Under Attack
Google has released a Chrome update to address a string of actively exploited vulnerabilities in 2026, including the seventh zero-day cased in the wild. The standout flaw is CVE-2026-87491, an out-of-bounds write in the V8 engine with a CVSS score of 8.8,…
-
Google Fixes Exploited Chrome Zero Day Among 230 Flaws in Version 153
Google released Chrome 153 to the stable channel on 9 September 2026, delivering fixes for 230 vulnerabilities and notably addressing a zero-day that is already being exploited in the wild. The CVE tracked as CVE-2026-87491 is described as an out-of-bounds…
-
Chrome Patches Exploited V8 Zero Day Allowing Code Execution
Google Chrome has patched a zero‑day vulnerability in its V8 JavaScript and WebAssembly engine that has been exploited in the wild. The flaw, CVE-2026-87491, is described as an out-of-bounds write in V8 that could let a remote attacker run arbitrary code…
-
Chrome 153 Patches Exploited V8 Zero Day and 229 Flaws
Google has released Chrome 153 to address 230 security flaws, including a zero-day vulnerability in the V8 JavaScript engine that is already being exploited in the wild. The flaw, CVE-2026-87491, is described as an out-of-bounds write in V8 that could allow…
-
-
ClickFix Campaign Hijacks Crypto Trades Through Malicious Browser Scripts
A campaign named ClickFix has moved from tricking users into running commands on their computers to convincing them to inject malicious JavaScript into their own browsers, with the aim of fraud in the cryptocurrency sector. Cisco Talos researchers published…
InfosecurityClickFix -
Cloudflare Rebuilds Workers’ Node.js Module Loading for Speed
Cloudflare has rebuilt the Node[.]js compatibility story for its Workers runtime by overhauling the module registry inside workerd, the core open‑source component of Workers. The aim is to make module loading faster, more standards‑compliant, and better…
Cloudflare
-
Compromised AI Agents and API Keys Now Lead Enterprise Intrusions
A new SpyCloud study claims that compromised non-human identities (NHIs), including AI agents, service accounts, API keys and authentication tokens, are now the number one entry point for hackers into enterprises. Based on a survey of 750 cybersecurity…
Infosecurity -
US agencies warn Chinese AI firms are distilling frontier models at scale
The NSA, CISA and FBI warn that Chinese AI firms are systematically “distilling” outputs from US frontier AI models to train their own systems. In a report cited by the agencies, DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun and Z[.]AI are said to have…
SecurityWeek
-
New Jersey School District Network Outage Linked to Ransomware Attack
Westfield Public Schools in New Jersey experienced a district-wide network outage during the first week of the new school year, initially attributed to equipment failure before officials said the cause remained under investigation. The district later…
DataBreachesINC Ransom -
Russian Web Developer Extradited to US Over Bank Account Takeovers
A Russian web developer, Sergei Anatolyevich Filimonov, 36, has been extradited from Georgia to the United States to face an indictment in a bank account takeover scheme. He appeared in a federal court in Atlanta on 4 September and has pleaded not guilty to…
DataBreaches -
SpyCloud Report Finds Non-Human Identities Lead Enterprise Attacks
SpyCloud has released its 2026 Identity Threat Report, which finds that non-human identities (NHIs) — including AI agents, service accounts, API keys and authentication tokens — are now the leading route into the modern enterprise. In the survey of 750…
SecurityOnline
-
Meta Unveils Muse AI Agent to Handle Users’ Everyday Tasks
Meta has rolled out Muse, a personal AI agent aimed at helping adults with day-to-day tasks such as scheduling, shopping, and long-term planning. The service is currently US-only and requires users to be 18 or older. Muse runs on a dedicated, secure virtual…
SecurityWeek -
Tines Shows How Security Teams Can Cut CVE Response Times
The Hacker News reports on a forthcoming expert webinar hosted by the Tines security team, framed around the challenge security operations teams face when a new CVE appears. The session, titled Outpacing AI-Era Attacks Starts With Faster Time to Answer,…
The Hacker News -
DeepSeek AI Coding Agent Flaw Let Attackers Disable Its Sandbox
A vulnerability in DeepSeek Harness allowed a sandboxed AI coding agent to disable its own sandbox without an extra approval prompt. The flaw arose because the tool’s local web interface, which the agent can reach from inside its environment, did not require…
-
ICS Patch Tuesday Fixes Critical Schneider, Siemens Flaws
Schneider Electric’s September 2026 Patch Tuesday advisory batch centres on its ICS portfolio, with four new advisories and updates to four others. The most critical flaw is an authentication vulnerability in the Modicon M580 and Modicon M580 Safety…
-
Alby Lightning Wallet Flaw Put Internet-Facing Hubs at Risk
Alby has disclosed a critical flaw in its Alby Hub self-hosted Lightning Wallet service that could have allowed an attacker to take over a wallet and siphon funds, but only if the Hub was exposed to the internet. The vulnerability affects Hub versions 1.7.0…
The Hacker News -
Ivanti Patches Critical Flaws Enabling Remote Code Execution
Ivanti has released security updates across three enterprise products—Neurons for ITSM, Sentry and Endpoint Manager Mobile (EPMM)—to address a set of critical and high-severity flaws. Neurons for ITSM accounts for the bulk of the fixes, with eight identified…
-
Microsoft Patches 964 CVEs as Two Windows Zero-Days Face Attacks
Microsoft’s September 2026 Patch Tuesday delivers what the vendor describes as the largest ever batch of fixes, addressing 964 CVEs, with 104 rated Critical and 860 rated Important. Microsoft notes 974 CVEs in total for the release, but ten affect cloud…
-
OfferLoader Campaign Hides Three Payloads Behind Fake Software Installers
Unit 42’s analysis tracks a pay-per-install (PPI) cybercrime operation dubbed CL-CRI-1171, active for at least two years and targeting a broad set of victims including young gamers, enterprise endpoints and government entities. The operation uses a single,…
unit42.paloaltonetworks.comLightBasin
-
Novel Phishing Campaign Hides Malicious Pages Inside Victims’ Browsers
SecurityWeek reports a novel phishing campaign that defeats traditional page-based defences by rendering the malicious page inside the victim’s browser using blob URLs. The operation starts with a Docusign-themed email that includes a calendar invite to…
SecurityWeek
-
Proposed ORKS Standard Could Make Leaked API Keys Self-Destruct
A SecurityWeek piece by Matt Honea discusses a proposed open standard to make leaked API keys self-destruct within minutes rather than hours or days. The concept, dubbed ORKS (Open Revocable Key Standard), aims to give every API key a built‑in mechanism for…
SecurityWeek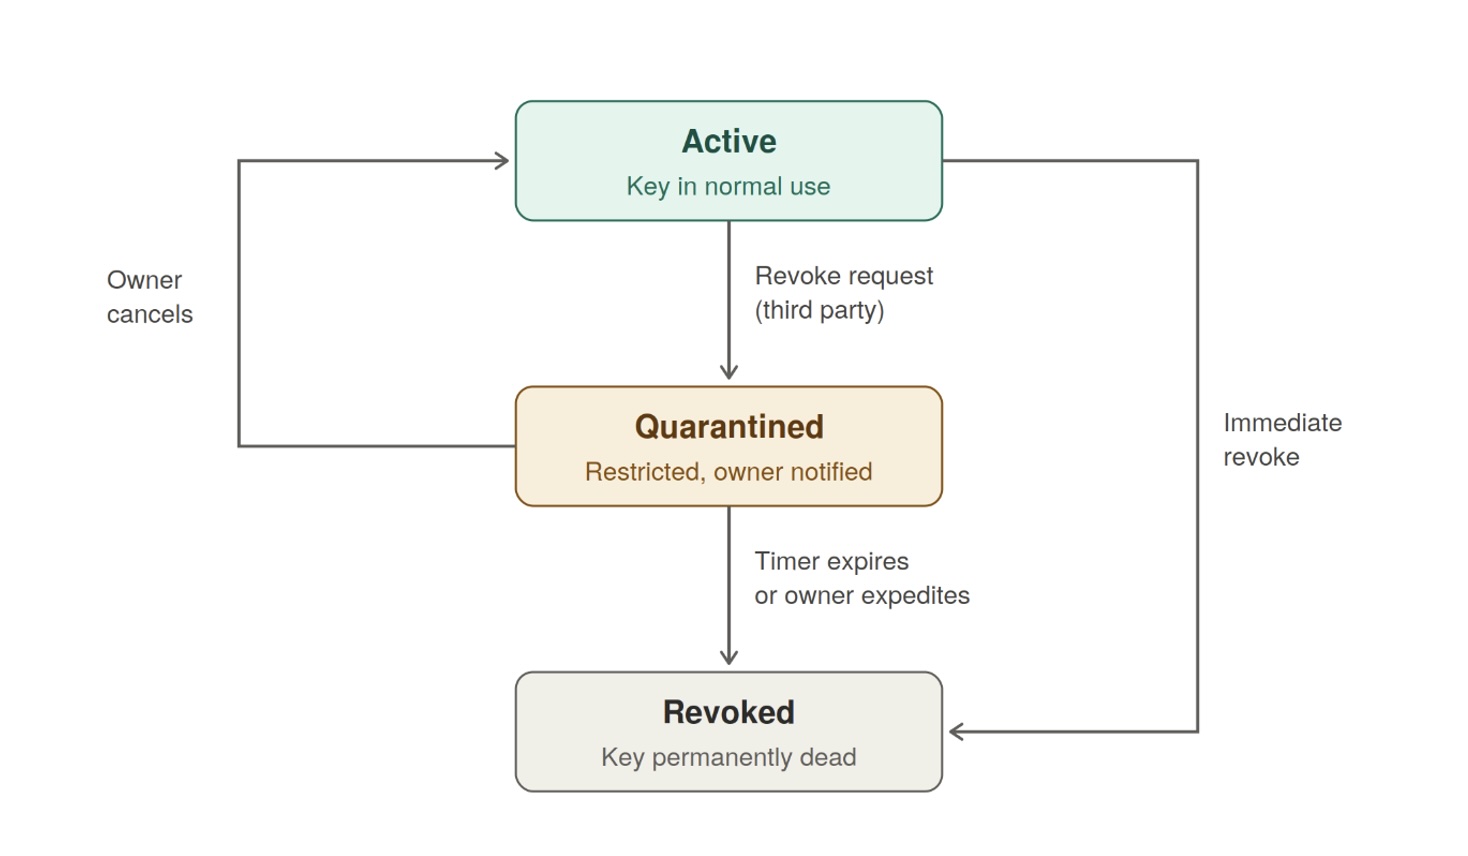
-
Microsoft Windows3 articles this day · The Hacker News first
Microsoft Patches Record 974 CVEs Amid Exploited Windows Zero-Days · Microsoft Fixes Nearly 1,000 Flaws in Record Patch Tuesday Update
-
Microsoft Patches Record 974 CVEs Amid Exploited Windows Zero-Days
Microsoft has reported a record-breaking 974 CVEs addressed in its September 2026 Patch Tuesday, shattering the previous high of 570 CVEs. The August–September trend shows a sharp rise in patched flaws, with Windows accounting for 723 CVEs and Office for…
-
Microsoft Fixes Nearly 1,000 Flaws in Record Patch Tuesday Update
Microsoft’s September 2026 Patch Tuesday set another record, with Microsoft stating fixes for up to 974 CVEs across Windows, Exchange, SharePoint, SQL Server and other services. The update slate includes two zero-days exploited in the wild and 20 wormable…
-
Microsoft Patches 974 Flaws as Two Windows Zero Days Exploited
Microsoft’s September Patch Tuesday set a new record, with fixes for 974 vulnerabilities across its software stack, including two flaws that were already being exploited in the wild. The breakdown cited by Microsoft shows 723 in Windows, 111 in Office and…
-
-
US Agencies Accuse Chinese AI Firms of Stealing Frontier Model Secrets
US cybersecurity and intelligence agencies have accused China-based AI firms of conducting industrial-scale distillation attacks to extract proprietary functionalities from U.S. frontier models. In a joint bulletin from the NSA, CISA and FBI, the agencies…
The Hacker News -
Google Overhauls EU Search Results to Meet DMA Self-Preference Rules
Google has announced a major overhaul of its European search results in response to regulatory pressure under the European Union’s Digital Markets Act (DMA). The move follows a summer where the EU fined Google a total of 890 million euros, with 460 million…
SecurityOnline
-
Cisco UCS Servers Face Secure Boot Bypass via Public Exploit
Cisco has disclosed a high-severity vulnerability affecting its Unified Computing System (UCS) platform that enables a Secure Boot bypass via the UEFI shell. The flaw, tracked as CVE-2026-20293 with a CVSS v3 score of 7.1, could allow an authenticated user…
-
F5 BIG-IP2 articles this day · The Hacker News first
Fileless PoisonedRefresh Rootkit Targets F5 BIG-IP APM Systems · F5 BIG-IP Flaw Hid In-Memory Web Shells from Disk Scans
-
Fileless PoisonedRefresh Rootkit Targets F5 BIG-IP APM Systems
SophosLabs published a technical analysis on 8 September 2026 describing PoisonedRefresh, a fileless Linux rootkit used against F5 BIG-IP APM environments. The rootkit operates in memory to inject a PHP web shell into the BIG-IP APM Apache process, leaving…
-
F5 BIG-IP Flaw Hid In-Memory Web Shells from Disk Scans
Sophos has analysed malware linked to intrusions into F5 BIG-IP Access Policy Manager appliances, which hides a PHP web shell in memory rather than on disk. The shell is injected when Apache loads any of three APM webtop PHP scripts: apm_css.php3,…
-
-
Google Fixes Critical Android Flaws Enabling Remote Code Execution
Google’s September 2026 Android security bulletin fixes a set of critical flaws across System, Framework and Kernel components, addressing remote code execution and privilege escalation risks. The bulletin confirms five CVEs in total, with one…
-
Meta launches Muse AI agent to automate shopping, travel and more
Meta has formally launched Muse, its end-to-end personal AI agent designed to act autonomously on a user’s behalf. Unlike prior conversational bots, Muse comes with its own dedicated app and web interface and operates without requiring technical know‑how.…
SecurityOnline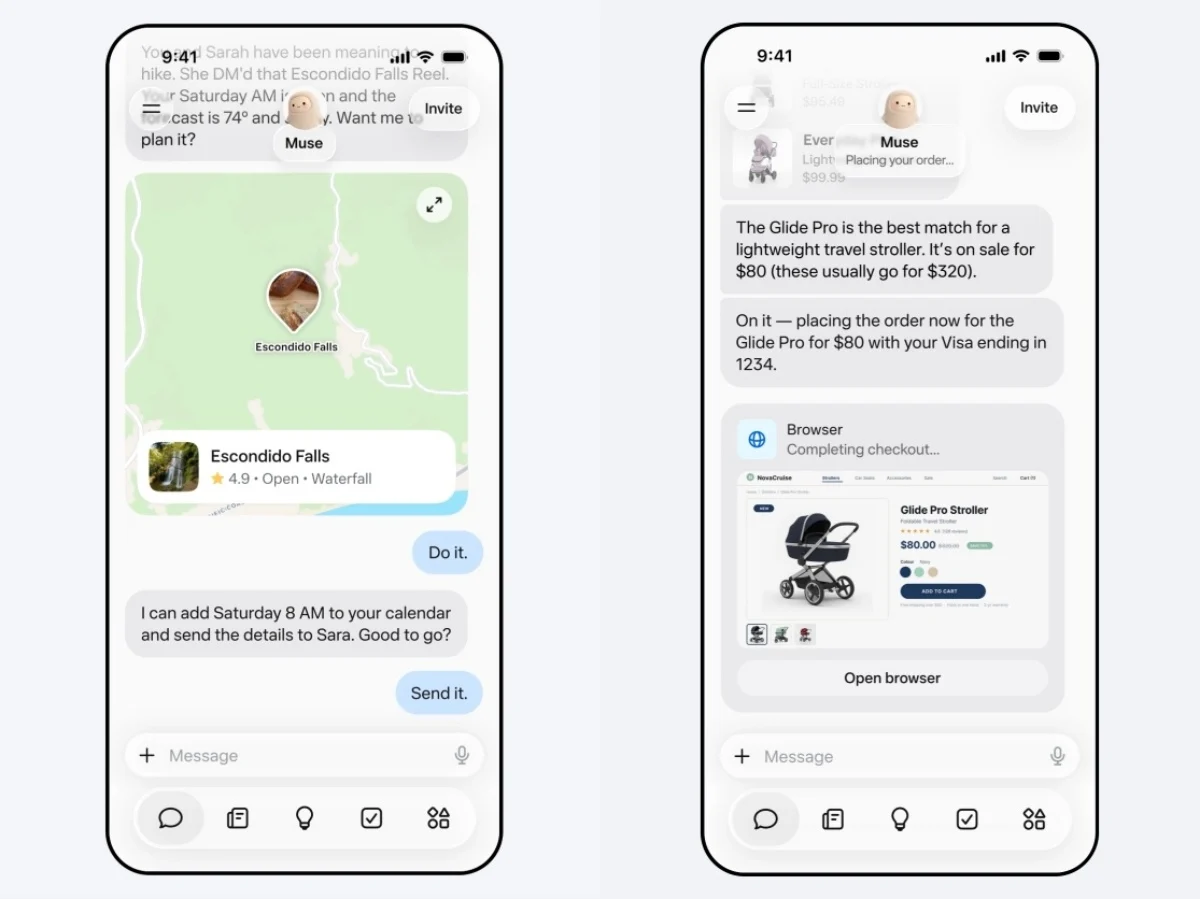
-
Australia’s ‘My Feed, My Way’ Bill Targets Algorithmic Platforms
Australia is advancing a new Digital Duty of Care that could reshuffle how social platforms present content. The government released draft legislation, labelled by Prime Minister Anthony Albanese as “My Feed, My Way,” which would allow Australians over 16 to…
Malwarebytes
-
WebPros cPanel2 articles this day · SecurityOnline first
Critical cPanel flaw lets email users escalate to root access · cPanel SQL Flaw Lets Privileged Accounts Seize Servers with Root Access
-
Critical cPanel flaw lets email users escalate to root access
A new cPanel vulnerability, tracked as CVE-2026-67401, could allow an authenticated hosting account with mail privileges to escalate to full root on the server. The flaw is described by cPanel as an SQL injection in the EmailTrack functionality, through…
-
cPanel SQL Flaw Lets Privileged Accounts Seize Servers with Root Access
CVE-2026-67401 is a newly disclosed SQL injection flaw in cPanel that could allow an attacker to gain full control of a server. The advisory describes an authenticated cPanel account holder with mail-related privileges who can abuse cPanel’s Email Track…
-
-
SAP_SE SAP Extended Passport (EPP) Processing2 articles this day · The Hacker News first
Over 10,000 SAP Systems Exposed to Critical Kernel Flaw · SAP Patches Critical SAP Flaws Enabling Unauthenticated RCE
-
Over 10,000 SAP Systems Exposed to Critical Kernel Flaw
Over 10,000 internet-facing SAP systems could be exposed to a maximum-severity vulnerability in the SAP kernel, according to Onapsis. The Onapsis Research Labs (ORL) disclosed the Memory Corruption vulnerability in SAP Extended Passport (EPP) Processing,…
-
SAP Patches Critical SAP Flaws Enabling Unauthenticated RCE
SAP has issued security updates to fix multiple high‑severity flaws, including a maximum‑severity remote, unauthenticated memory corruption vulnerability in the SAP kernel’s Extended Passport (EPP) processing, tracked as CVE-2026-44756 (CVSS 10.0), codenamed…
-
-
Fake macOS Installers Hide OtterCookie Backdoor in North Korean Campaign
Security researchers have identified a campaign in which fake macOS installers masquerade as legitimate utilities to deliver a backdoor known as OtterCookie. The attackers have trojanised disk images (DMG) and installer packages (PKG) that impersonate apps…
SecurityOnlineContagious Interview
-
Microsoft Bets on Local AI to Deliver ‘Unmetered Intelligence’ in Windows 11
Microsoft used the IFA 2026 event to push its vision of “unmetered intelligence” for Windows 11, reviving Bill Gates’ desk‑top promise with a heavy emphasis on local AI processing. The company says frontier AI models will still need substantial cloud…
SecurityOnline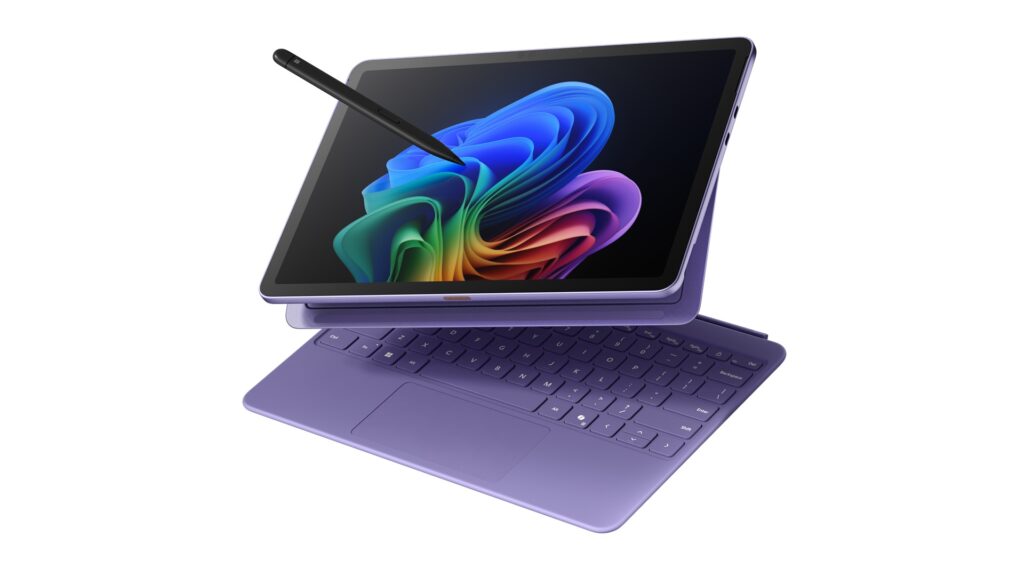
-
OpenAI’s Images 2.5 Speeds Up Generation and Sharpens Editing
OpenAI has unveiled Images 2.5, the latest iteration of its image-generation model, promising better image detail, more precise editing, improved reference-photo consistency, and faster generation. The firm states that ChatGPT Images and the GPT-Image family…
SecurityOnline
-
Microsoft Malware Protection Engine3 articles this day · SecurityOnline first
ShieldCrash PoC Revives Microsoft Defender SYSTEM File Read Flaw · Microsoft Defender Zero Day Bypasses Patch to Read Windows Files as SYSTEM
-
ShieldCrash PoC Revives Microsoft Defender SYSTEM File Read Flaw
Security researcher Chaotic Eclipse (INFINITE NIGHTMARE, MSNightmare, Nightmare-Eclipse) released a new zero-day exploit named ShieldCrash, a PoC that demonstrates an arbitrary file read as SYSTEM in Microsoft Defender. The PoC targets a vulnerability…
-
Microsoft Defender Zero Day Bypasses Patch to Read Windows Files as SYSTEM
A security researcher going by Chaotic Eclipse has released a proof-of-concept demonstrating a new zero-day in Microsoft Defender, named ShieldCrash. The PoC suggests it bypasses the previously patched ShieldBreak vulnerability, CVE-2026-69414 (CVSS 7.8), by…
-
Microsoft Defender 0day PoC Exposes SYSTEM Files on Windows
A publicly available 0day in Microsoft Defender, dubbed ShieldCrash, has been disclosed with a working PoC that can read arbitrary files as SYSTEM on all supported Windows versions. The flaw is associated with CVE-2026-69414 and follows an initial…
-
-
Microsoft 365 Flaw Lets Spoofed Internal Emails Bypass Protection
Researchers have identified an active bypass of Microsoft 365’s RejectDirectSend control that enables spoofed internal emails to reach recipients. The flaw uses an empty SMTP envelope sender, allowing external senders to deliver unauthenticated messages that…
SecurityOnline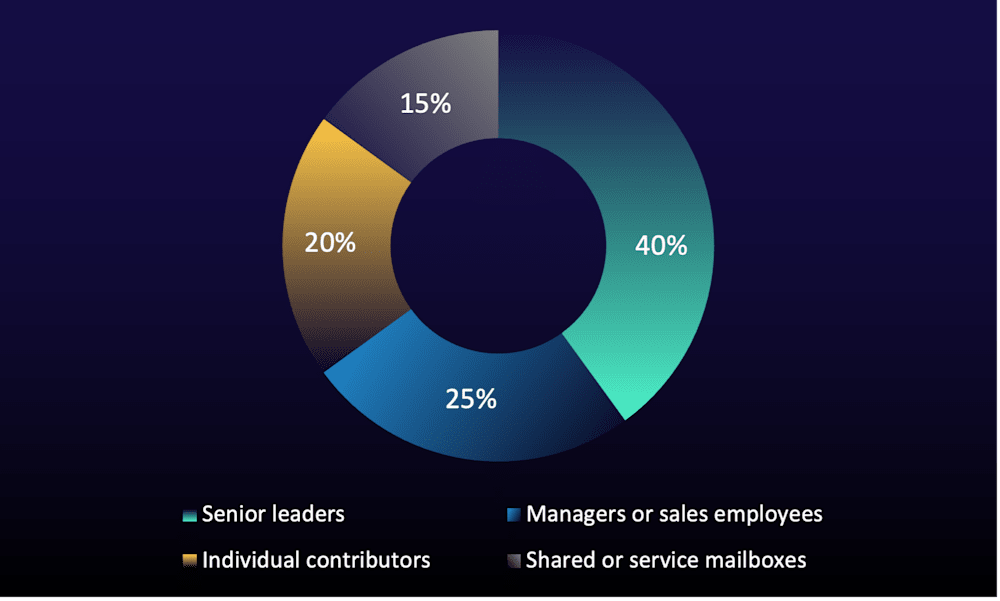
-
CISA Warns Attackers Are Exploiting N-able N-central Flaw
CISA has added a highly severe flaw in N-able N-central to its Known Exploited Vulnerabilities catalogue, marking it as a pre-authentication remote code execution (RCE) that could be exploited without user credentials. The issue, CVE-2026-86218 (CVSS 10.0),…
-
Windows 11 Previews Tease Automatic Theme Switching at Sunset
Windows 11 preview builds are teasing a long-awaited improvement: automatic light and dark theme switching. The article notes that hidden strings in the latest Windows 11 test builds describe a feature to alternate between light and dark modes, with the…
SecurityOnline
-
Apache Impala Flaws Let Attackers Seize Analytics Clusters Remotely
Apache Impala has four high-severity vulnerabilities that could let attackers take remote control of large analytics clusters. The flaws include an authentication bypass and remote code execution, along with server-side request forgery (SSRF) issues. The…
-
Asahi Linux Brings Apple M3 Support to Kernel 7.2, With Major Gaps
Asahi Linux has announced progress in bringing support for Apple’s M3-series chips, with the first M3 platform code now merged upstream in Linux kernel 7.2. After extensive reverse engineering, developers report that many functions already present on M1 and…
SecurityOnline
-
Critical Predis Flaw Lets Attackers Smuggle Commands into Redis
Security researchers have disclosed a critical vulnerability in the Predis PHP client for Redis, tracked as CVE-2026-84372. The flaw, rated CVSS 9.8 (Critical), has public PoC exploit code and is tied to a CRLF (carriage return line feed) sequence in the…
-
Critical MapLibre Flaw Enables Zero-Click XSS in Map Apps
MapLibre GL JS has a critical XSS flaw, CVE-2026-85061, affecting applications that render untrusted map styles or custom attributions. The vulnerability sits in the library prior to version 6.4.1 and is described as a sanitizer bypass in DOM[.]sanitize()…
-
ISC Stormcast For Wednesday, September 9th, 2026 https://isc.sans.edu/podcastdetail/10086, (Wed, Sep 9th)
(c) SANS Internet Storm Center. https://isc.sans.edu Creative Commons Attribution-Noncommercial 3.0 United States License.
SANS ISC -
Google Doubles Chrome Release Speed With New Biweekly Updates
Google has announced a shift to a two‑week release cadence for Chrome, beginning with Chrome 153 released on 9 September 2026 across Windows, macOS, Android and iOS. The move shortens the previous four‑week cycle introduced in 2021 to a biweekly pattern,…
SecurityOnline
-
3,562 Exposed Redis Servers Hijacked in Rogue Replication Attack
Researchers from Hunt[.]io uncovered a Redis-based cryptomining operation that compromised 3,562 internet-facing Redis servers, largely on APAC cloud hosts. The attacker used a rogue replication method to point victims at a fake Redis master, delivering a…
SecurityOnline
-
CVE-2026-41870: Unauthenticated RCE in Apache Nutch
The page reports on four critical vulnerabilities detected in various software. Key points include: 1. **CVE-2026-75650**: An Adobe Commerce and Magento vulnerability concerning improper neutralization of special template elements. 2. **CVE-2026-81963**: A…
-
Siemens Flaws Let Attackers Hijack Accounts and Gain Root Access
Siemens ProductCERT disclosed two critical vulnerabilities affecting Industrial Edge and Siveillance Open Interface Services (OIS) on 8 September 2026. The flaws carry CVSS scores above 9.0. The first, CVE-2026-18963, resides in the password reset flow of…
-
Critical Hawtio Operator Flaw Enables Cross Tenant Impersonation and RCE
Red Hat has flagged a critical vulnerability in Hawtio Operator used with Kubernetes and OpenShift. Identified as CVE-2026-78234 and rated CVSS 9.9, the flaw affects Hawtio-operator installations that rely on the OpenShift Service CA for client…
-
AI-Assisted Attacks Target Latin American Transport and Banks
Palo Alto Networks Unit 42 reports two AI-assisted intrusion campaigns targeting Latin American organisations, with activity spanning Mexico, Ecuador and Brazil. In both cases, attackers leveraged commercial large language models to script or enhance…
SecurityOnline