News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Sat 24 Oct· 3 articles
-
Collabora Online - Built-in CODE Server2 articles this day · The Hacker News first
CISA Flags Exploited Collabora Online Flaw for Urgent Patching · CISA Warns of Active Attacks on Nextcloud and Arista Flaws
-
CISA Flags Exploited Collabora Online Flaw for Urgent Patching
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical flaw in Collabora Online’s Built-in CODE Server to its Known Exploited Vulnerabilities (KEV) catalogue. The vulnerability, tracked as CVE-2026-110447, is an OS command…
-
CISA Warns of Active Attacks on Nextcloud and Arista Flaws
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two actively exploited vulnerabilities to the Known Exploited Vulnerabilities (KEV) catalog, affecting Collabora Online Built-in CODE Server and Arista VeloCloud Orchestrator (VCO).…
-
-
CISA flags exploited Arista VeloCloud flaw that lets attackers impersonate superusers
U.S. CISA has added a critical vulnerability in Arista’s VeloCloud Orchestrator (VCO) to its Known Exploited Vulnerabilities (KEV) catalog. The flaw, tracked as CVE-2026-114625 with a CVSS score of 9.4, affects on‑premises VCO deployments and is linked to a…

Fri 23 Oct· 8 articles
-
CISA Flags Actively Exploited Nextcloud Code Injection Flaw
CISA added CVE-2026-110447 to its Known Exploited Vulnerabilities (KEV) catalogue on 23 October 2026. The flaw affects Collabora Online – Built-in CODE Server when used within the Nextcloud platform and can allow remote code execution through OS command…
-
Arista Networks VeloCloud Orchestrator3 articles this day · SOCRadar first
CISA Confirms Active Attacks on Arista VeloCloud Orchestrator · Arista VeloCloud Flaw Marks Third Exploited Orchestrator Zero-Day
-
CISA Confirms Active Attacks on Arista VeloCloud Orchestrator
CISA added CVE-2026-114625, the Arista VeloCloud Orchestrator SQL Injection Vulnerability, to its Known Exploited Vulnerabilities (KEV) catalogue on 23 October 2026. The flaw affects on-premises Arista VeloCloud Orchestrator and may let a remote attacker…
-
Arista VeloCloud Flaw Marks Third Exploited Orchestrator Zero-Day
Arista Networks has released patches for a third exploited zero-day in its VeloCloud Orchestrator (VCO), a central management tool used in software-defined networking. The vulnerability, tracked as CVE-2026-114625, is a critical SQL injection that can be…
-
Arista VeloCloud Orchestrators Hit by Exploited SQL Injection Flaw
Arista has disclosed CVE-2026-114625, a critical SQL injection flaw in on-prem VeloCloud Orchestrator (VCO) deployments. The vulnerability, which is being actively exploited in the wild, allows any authenticated portal user—even an Enterprise Read Only…
-
-
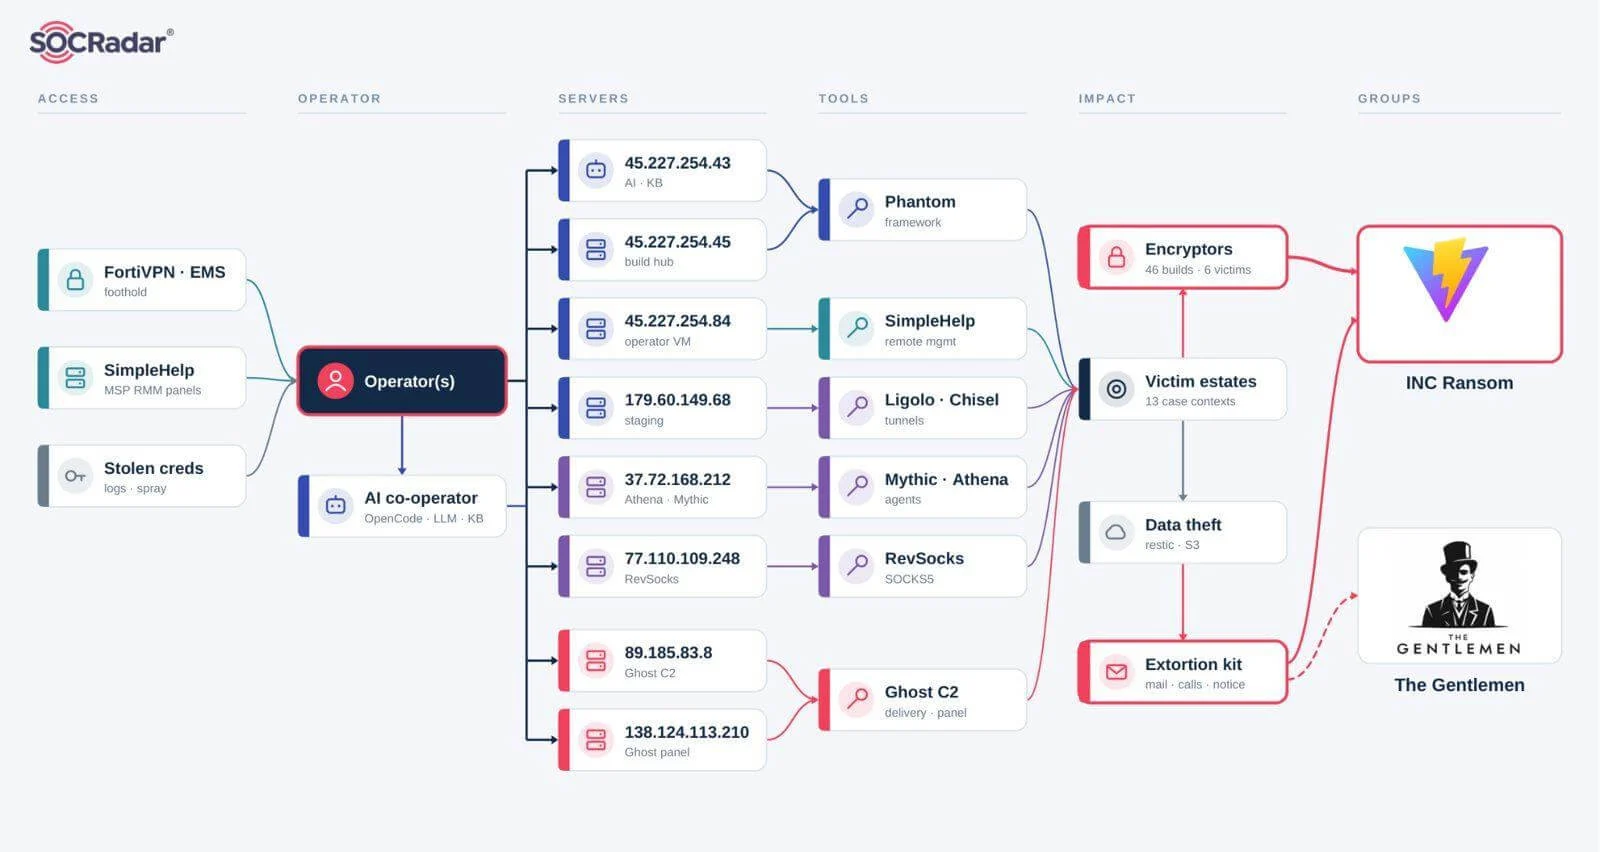
AI Agents Power Ransomware Affiliates’ Attacks on Edge Devices
Cybersecurity researchers have uncovered an AI-driven intrusion ecosystem operated by affiliates of the INC and The Gentlemen ransomware groups. Central to the operation is an Autonomous Red Team Kill Chain Framework called Phantom, used in live operations…
-
Fortinet FortiWeb2 articles this day · SecurityOnline first
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign · Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
-
Hackers Target Exposed Fortinet and Palo Alto Firewalls in Global Campaign
Cybersecurity researchers have detailed a large-scale campaign that targeted exposed network edge devices, including Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. The joint investigation by Group-IB and NyxLab notes that operators in the…
-
Hackers Steal 70,000 Credentials in Fortinet and Palo Alto Attacks
Group-IB and NyxLab have uncovered a widespread campaign linked to an operator known as “k0t” that targets FortiGate, FortiWeb and Palo Alto GlobalProtect deployments. Launched largely between February and June 2026, the operation uses bulk asset discovery…
-
-
INC Ransomware Exposed Using AI and Custom Malware Against Victims
In late September 2026, security researchers uncovered seven INC Ransomware command servers that exposed AI-driven activity and bespoke malware used by affiliates of the group. The exposed AI workbench contained 8,257 messages across 133 OpenCode sessions…
Thu 22 Oct· 3 articles
-
Arista Networks VeloCloud Orchestrator2 articles this day · SecurityOnline first
Arista VeloCloud Zero Day Exploited to Gain Superuser Access · Arista VeloCloud flaw under attack lets users seize superuser access
-
Arista VeloCloud Zero Day Exploited to Gain Superuser Access
Arista has disclosed a critical zero-day vulnerability in its VeloCloud Orchestrator (VCO) that is being exploited in the wild. The flaw, tracked as CVE-2026-114625 and rated 9.9 on the CVSS scale, is a SQL injection that can be exploited by anyone who can…
-
Arista VeloCloud flaw under attack lets users seize superuser access
Arista has disclosed that CVE-2026-114625, a critical SQL injection vulnerability in the VeloCloud Orchestrator (VCO), is being exploited in the wild. The flaw, rated CVSS 9.9, allows any authenticated user to escalate to a local “superuser operator” by…
-
-
AI Assisted PaperCut Campaign Breaches 395 Organisations Worldwide
Hunt[.]io researchers uncovered three open directories on an attacker server involved in a PaperCut RCE campaign, exposing AI-assisted exploitation toolkit elements and victim data from hundreds of targets. The exposed material includes AI agent…
Tue 20 Oct· 16 articles
-
Siemens Software Center4 articles this day · SecurityOnline first
CISA Flags Actively Exploited Siemens Software Center Flaw · Attackers exploit Siemens Software Center flaw to spread malware via ClickFix
-
CISA Flags Actively Exploited Siemens Software Center Flaw
CISA added CVE-2026-110936 to its Known Exploited Vulnerabilities (KEV) catalogue on 20 October 2026. The vulnerability affects Siemens Software Center and is an uncontrolled search path element flaw that could let an authenticated local attacker execute…
-
Attackers exploit Siemens Software Center flaw to spread malware via ClickFix
Siemens has warned customers that attackers are actively exploiting a dynamic link library (DLL) side-loading flaw in its Software Center to distribute malware. The activity is linked to the Romulus multi-platform ClickFix campaign, a server hosting panel…
-
Siemens Patches Software Center Flaw Exploited in ClickFix Attacks
Siemens has disclosed and patched a DLL sideloading flaw in its Software Center that has been actively exploited in ClickFix campaigns. Tracked as CVE-2026-110936 (CVSS v4 score: 8.4), the vulnerability arises because the affected application loads DLLs from…
-
Hackers Exploit Siemens Software Center Flaw to Hide Malware
Siemens confirms that CVE-2026-110936, a DLL sideloading flaw in Siemens Software Center, is being exploited in the wild. The vulnerability allows attackers to load malicious DLLs through an uncontrolled search path, disguising malware as a legitimate,…
-
-
CISA Flags Actively Exploited Plex Server SSRF Flaw
CISA added CVE-2026-96652 to its Known Exploited Vulnerabilities (KEV) catalogue on 20 October 2026. The vulnerability affects Plex Media Server and is a server-side request forgery (SSRF) flaw that can make the server send a POST request to a destination…
-
CISA Flags Actively Exploited Plex Media Server Flaw for Patching
CISA added CVE-2026-96654 to its Known Exploited Vulnerabilities (KEV) catalogue on 20 October 2026. The flaw affects Plex Media Server and could let an attacker call functions belonging to other plugins and supply their own parameters. The vulnerability,…
-
CISA Flags Exploited Plex Flaw That Can Reach Internal Systems
CISA added CVE-2026-96655 to its Known Exploited Vulnerabilities (KEV) catalogue on 20 October 2026. The vulnerability affects Plex Media Server and is a server-side request forgery (SSRF) flaw that could let an authenticated user make the server request…
-
CISA Confirms Active Exploitation of Plex Media Server Flaw
CISA added CVE-2026-96656 to its Known Exploited Vulnerabilities (KEV) catalogue on 20 October 2026. The vulnerability affects Plex Media Server and is an external control of file name or path flaw that can let an admin user write arbitrary files that may…
-
CISA Flags Exploited SiteGuard Flaw That Could Give Attackers System Control
CISA added CVE-2026-106931 to its Known Exploited Vulnerabilities (KEV) catalogue on 20 October 2026. The vulnerability affects EG Secure Solutions SiteGuard Server Edition and is an OS command injection flaw that may let an attacker run arbitrary operating…
-
Palo Alto Networks PAN-OS3 articles this day · SecurityOnline first
Ransomware gangs exploit patched Palo Alto VPN security flaw · Qilin and INC ransomware gangs exploit Palo Alto VPN flaw to bypass MFA
-
Ransomware gangs exploit patched Palo Alto VPN security flaw
Palo Alto Networks has disclosed that exploitation of a vulnerability in PAN-OS and Prisma Access continues to be observed by ransomware actors, despite the flaw being patched earlier this year. The flaw, tracked as CVE-2026-0257, is an authentication bypass…
-
Qilin and INC ransomware gangs exploit Palo Alto VPN flaw to bypass MFA
Palo Alto Networks has disclosed that exploitation of a patched PAN-OS and Prisma Access flaw, CVE-2026-0257 (CVSS 7.8), is continuing in financially motivated campaigns. The vulnerability is an authentication bypass that could allow attackers to establish…
-
Ransomware gangs bypass MFA through PAN OS VPN flaw CVE-2026-0257
Ransomware groups are abusing CVE-2026-0257, a GlobalProtect authentication bypass in PAN-OS, to gain VPN access without valid credentials and to bypass MFA safeguards. The exposed flaw lets attackers skip login checks on vulnerable GlobalProtect portals and…
-
-
AI Agents Target 1,200 Retail Sites in Low Cost Hacking Campaign
A security researcher has watched attackers deploy autonomous AI agents against more than 1,200 retail and service websites, with at least 100 organisations affected. The activity centred on Cairn, an open‑source AI tool, whose exposed control panels were…
-
Japan’s October Breach Wave Exposes Millions of Customer Records
SOCRadar documents a dense wave of Japanese breach disclosures that began in late September and surged through October 2026. The firm’s Dark Web News logged 134 Japan-related items in the first half of October, more than all of September (129) and at roughly…
-
AI-Driven Ransomware Campaign Targeted 62 Organisations
SOCRadar Threat Research Unit (STRU) has disclosed an AI-driven intrusion ecosystem operated by affiliates of INC Ransomware and The Gentlemen Ransomware. A publicly accessible command-and-control server exposed the operators’ AI session databases, their…
-
APT28 Breaches NATO Naval Shipbuilder and Steals Credentials in Week-Long Intrusion
The Hacker News reports that the Russia-linked APT28 group, also known as BlueDelta, Fancy Bear or Forest Blizzard, has been attributed by Symantec Threat Hunter Team (Swallowtail) with breaching multiple NATO-related targets, including a naval shipbuilder…
Mon 19 Oct· 12 articles
-
Plex Media Server4 articles this day · SecurityOnline first
Attackers exploit Plex2Shell flaws to hijack servers for mining and proxying · Hackers exploit Plex flaws to install crypto miners and Linux backdoors
-
Attackers exploit Plex2Shell flaws to hijack servers for mining and proxying
Attackers are leveraging a vulnerability chain dubbed Plex2Shell that targets exposed Plex Media Server instances to deploy crypto mining and proxy software. On 16 October 2026, security researcher Zach Main published technical details and PoC code for the…
-
Hackers exploit Plex flaws to install crypto miners and Linux backdoors
Threat actors are actively exploiting a chain of Plex Media Server flaws, collectively dubbed Plex2Shell, to install crypto miners and a Linux proxy backdoor. In-the-wild activity follows a public PoC and chains four vulnerabilities to achieve…
-
Attackers Exploit Plex2Shell Flaws to Install Miners and Proxy Software
Threat actors have been observed delivering cryptocurrency miners and proxy software.
-
Attackers Exploit Plex Flaws to Run Cryptominers and Proxy Tools
Attackers have begun exploiting Plex Media Server vulnerabilities in the wild, following a full write-up and PoC by researcher Zach Main on 17 October 2026. The exploit chain, dubbed Plex2Shell, combines four CVEs to achieve unauthenticated remote code…
-
-
Attackers Exploited Siemens Software Center Flaw in Malware Campaign
Siemens has disclosed that threat actors exploited a vulnerability in its Software Center—tracked as CVE-2026-110936—as part of a malware campaign. The flaw arises because Software Center does not adequately restrict the folders it searches for DLL files,…
-
Citrix NetScaler ADC2 articles this day · Cloudflare first
Attackers chained two Citrix NetScaler flaws to gain root access and steal keys · Citrix NetScaler Flaw Sparks Attacks, Prompting Urgent Patching
-
Attackers chained two Citrix NetScaler flaws to gain root access and steal keys
In October 2026, Rapid7 disclosed a compromise of a Citrix NetScaler ADC appliance running a 14.1 build, where attackers exploited a chaining sequence involving CVE-2026-88771 and CVE-2026-88779. The intrusion achieved root code execution starting from…
-
Citrix NetScaler Flaw Sparks Attacks, Prompting Urgent Patching
Cloudflare reviews the crisis following a major vulnerability in Citrix NetScaler that enabled unauthenticated remote command execution via the login surface, with patches issued by Citrix and an emergency WAF rule from Cloudflare. The exploit disclosures…
-
-
BeyondTrust Remote Support3 articles this day · SecurityOnline first
BeyondTrust Remote Support flaw exploited before disclosure enabled file access · Attackers Exploited BeyondTrust Zero Day as Crypto Wallets Were Backdoored
-
BeyondTrust Remote Support flaw exploited before disclosure enabled file access
CVE-2026-102764 is a critical authentication bypass in BeyondTrust Remote Support (RS) that was exploited in the wild before a full disclosure. The flaw allows unauthenticated remote attackers to perform file operations on an affected RS appliance without…
-
Attackers Exploited BeyondTrust Zero Day as Crypto Wallets Were Backdoored
The Hacker News’s weekly recap highlights a week thick with high-stakes cyber incidents and disclosures across software, hardware and AI-enabled systems. Notably, BeyondTrust Remote Support was exploited as a zero-day in late August 2026 (CVE-2026-102764),…
-
Actively Exploited Flaws Hit Cisco, BeyondTrust and WordPress Plugin
Between 12 and 18 October 2026, CVE Watchtower logged 5,499 new vulnerabilities, with this weekly review tracking 12 exploited flaws. Six of those were flagged by Daily Cybersecurity’s intelligence sources, and three of the exploited flaws are not yet…
-
-
Fortinet Flaw Exploits Led to Stealthy FortiGate Implant in Telecom Breach
Security researchers have linked a sequence of exploited Fortinet vulnerabilities to a stealthy FortiGate implant used in a telecom intrusion. The activity began with the exploitation of a critical remote code execution flaw in FortiManager, tracked as…
-
Attackers Exploit SiteGuard WAF Flaw to Gain Root Access
Attackers are actively exploiting CVE-2026-106931 in SiteGuard Server Edition, a vulnerabilities disclosed by EG Secure Solutions and referenced by JVN. The flaw is an OS command injection that, once successfully exploited, lets an attacker run commands with…
Sat 17 Oct· 1 article
-
CISA Flags Fortinet and BeyondTrust Flaws Under Active Attack
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: Fortinet Multiple Products Path Traversal (CVE-2025-61624) and BeyondTrust Remote Support Authentication…
Fri 16 Oct· 12 articles
-
BeyondTrust Remote Support7 articles this day · The Hacker News first
China-linked hackers exploited BeyondTrust zero-day to steal credentials · CISA Warns of Exploited BeyondTrust Remote Support Auth Bypass
-
China-linked hackers exploited BeyondTrust zero-day to steal credentials
Ivanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
-
CISA Warns of Exploited BeyondTrust Remote Support Auth Bypass
CISA added CVE-2026-102764 to its Known Exploited Vulnerabilities (KEV) catalogue on 16 October 2026. The flaw affects BeyondTrust Remote Support and is an authentication bypass by spoofing that could let a remote attacker perform file operations on the…
-
BeyondTrust Patches Zero-Day Flaw Used to Gain Root Access
BeyondTrust disclosed CVE-2026-102764, a critical improper origin validation vulnerability (CWE-290) in its internal Remote Support messaging component. The flaw allowed remote attackers to trigger file operations without authentication or user interaction…
-
Chinese APT exploited BeyondTrust Remote Support flaw to steal files
A Chinese state‑sponsored APT, Armory Castle (UNC5221/Warp Panda), has been exploiting a BeyondTrust Remote Support vulnerability as a zero‑day since August 2026. The flaw, CVE-2026-102764, allows improper validation of message origins and could enable a…
-
China-Linked Hackers Exploited BeyondTrust Flaw to Install Root Backdoor
A suspected China state-backed actor, Armory Castle, exploited a newly disclosed critical vulnerability in BeyondTrust Remote Support, CVE-2026-102764, to gain access and escalate privileges on affected appliances. Google warns this allowed the group to…
-
BeyondTrust Patches Remote Access Flaw Exploited to Steal Credentials
BeyondTrust disclosed a critical remote-access vulnerability in its BeyondTrust Remote Support product, tracked as CVE-2026-102764, with a CVSS of 9.3. The flaw allows unauthenticated remote attackers to bypass origin validation in internal messaging…
-
China Linked Hackers Exploited BeyondTrust Zero Day to Steal Credentials
China-linked threat group Armory Castle, also known as UNC5221 or Warp Panda, exploited a zero-day in BeyondTrust Remote Support (formerly Bomgar) to compromise a self-hosted appliance in late August 2026. The flaw, tracked as CVE-2026-102764, is rated 9.3…
-
-
Fortinet FortiOS2 articles this day · The Hacker News first
CISA Flags Fortinet Path Traversal Flaw Under Active Exploitation · Fortinet flaw lets stealthy PEERSTITCH malware hijack firewall processes
-
CISA Flags Fortinet Path Traversal Flaw Under Active Exploitation
CISA added CVE-2025-61624 to its Known Exploited Vulnerabilities (KEV) catalogue on 16 October 2026. The vulnerability affects Fortinet FortiOS, FortiPAM, FortiProxy and FortiSwitchManager, and may let an authenticated administrator with at least read-write…
-
Fortinet flaw lets stealthy PEERSTITCH malware hijack firewall processes
Security researchers say attackers leveraged Fortinet FortiOS vulnerability CVE-2025-61624 to deploy a memory-resident ARM64 malware named PEERSTITCH. The flaw is a path traversal bug in the FortiOS command line interpreter that could let a privileged…
-
-
CISA Warns Atlassian Data Center Flaw Is Under Active Attack
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added an Atlassian flaw, CVE-2026-21589, to its Known Exploited Vulnerabilities (KEV) catalog. The vulnerability is described as a critical arbitrary file access flaw in Atlassian Data…
-
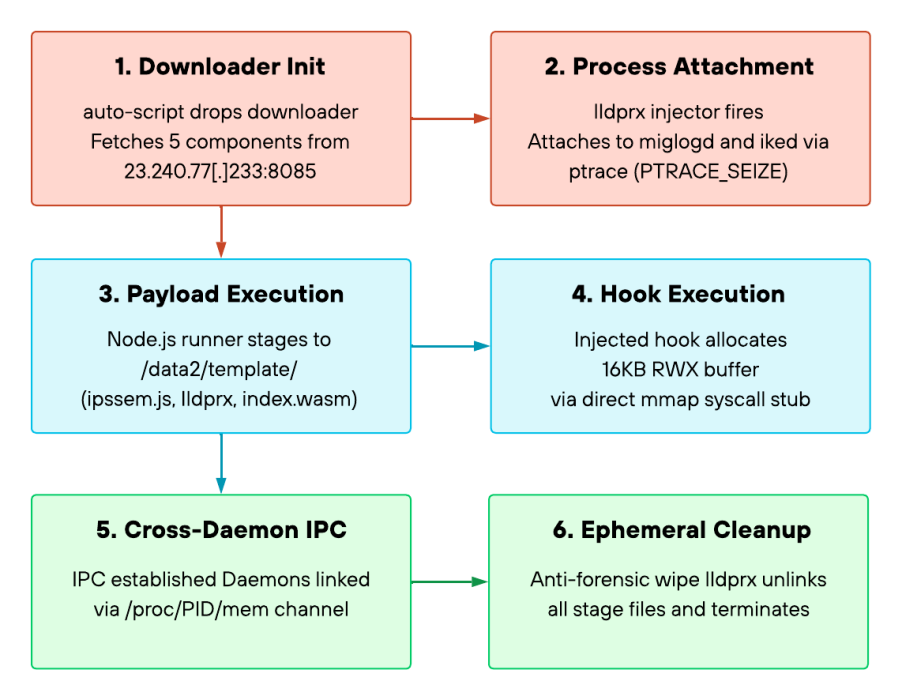
Hackers Stole Fortinet Credentials from 500 Firewalls via FortiManager
PEERSTITCH malware: How attackers compromised 500 Fortinet firewalls via FortiManager discusses a multi-stage intrusion disclosed by Palo Alto Networks Unit 42. The operation began in September 2024 when attackers exploited CVE-2024-47575 (FortiJump) to…
-
Espionage Group Exploits WinRAR Flaw to Target CIS Governments
Security researchers have publicised an active espionage campaign attributed to the UAT-6275 group (also tracked as TAG-193) targeting CIS governments and allied institutions. The campaigns ran from June 2025 to August 2026, culminating in four distinct…