News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Wed 9 Sep· 29 articles
-
Hackers Use Fake IT Calls to Hijack Microsoft 365 Accounts
Hackers are targeting senior Microsoft 365 accounts with highly tailored vishing campaigns that mimic internal IT helpdesk calls. The PREY-0058 operation, which aligns with UNC6671/BlackFile in some threat intelligence, starts with a phone call to executives…
SecurityOnlineUNC6671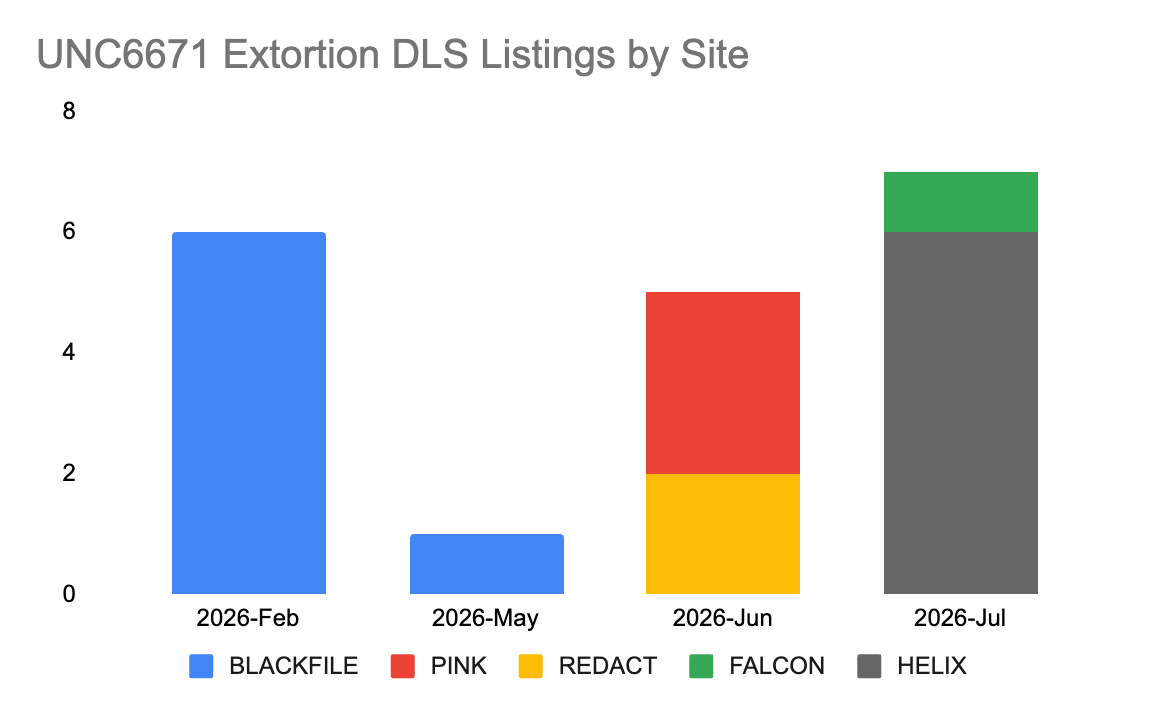
-
Palo Alto Firewalls Exposed to Root Code Execution Flaw in PAN-OS
On 9 September 2026, Palo Alto Networks disclosed a high-severity vulnerability in PAN-OS (CVE-2026-0310) that could allow unauthenticated remote attackers to execute arbitrary code with root privileges or cause a denial of service. The flaw resides in the…
-
Cisco Warns Attackers Are Exploiting Critical FMC Flaws for Root Access
Cisco Talos researchers say two critical flaws in Cisco Secure Firewall Management Center (FMC) are being actively exploited in the wild. The vulnerabilities are CVE-2026-20079, an authentication bypass in the FMC web interface, and CVE-2026-20316, a flaw…
-
GnuTLS CI Leak Exposed GitLab Token With Owner Access to 55 Projects
Truffle Security researchers detected a critical token leak tied to GnuTLS in June 2026, exposing a GitLab personal access token used by a public CI artifact. The token carried api scope and Owner privileges across 55 open‑source projects, including GnuTLS,…
SecurityOnline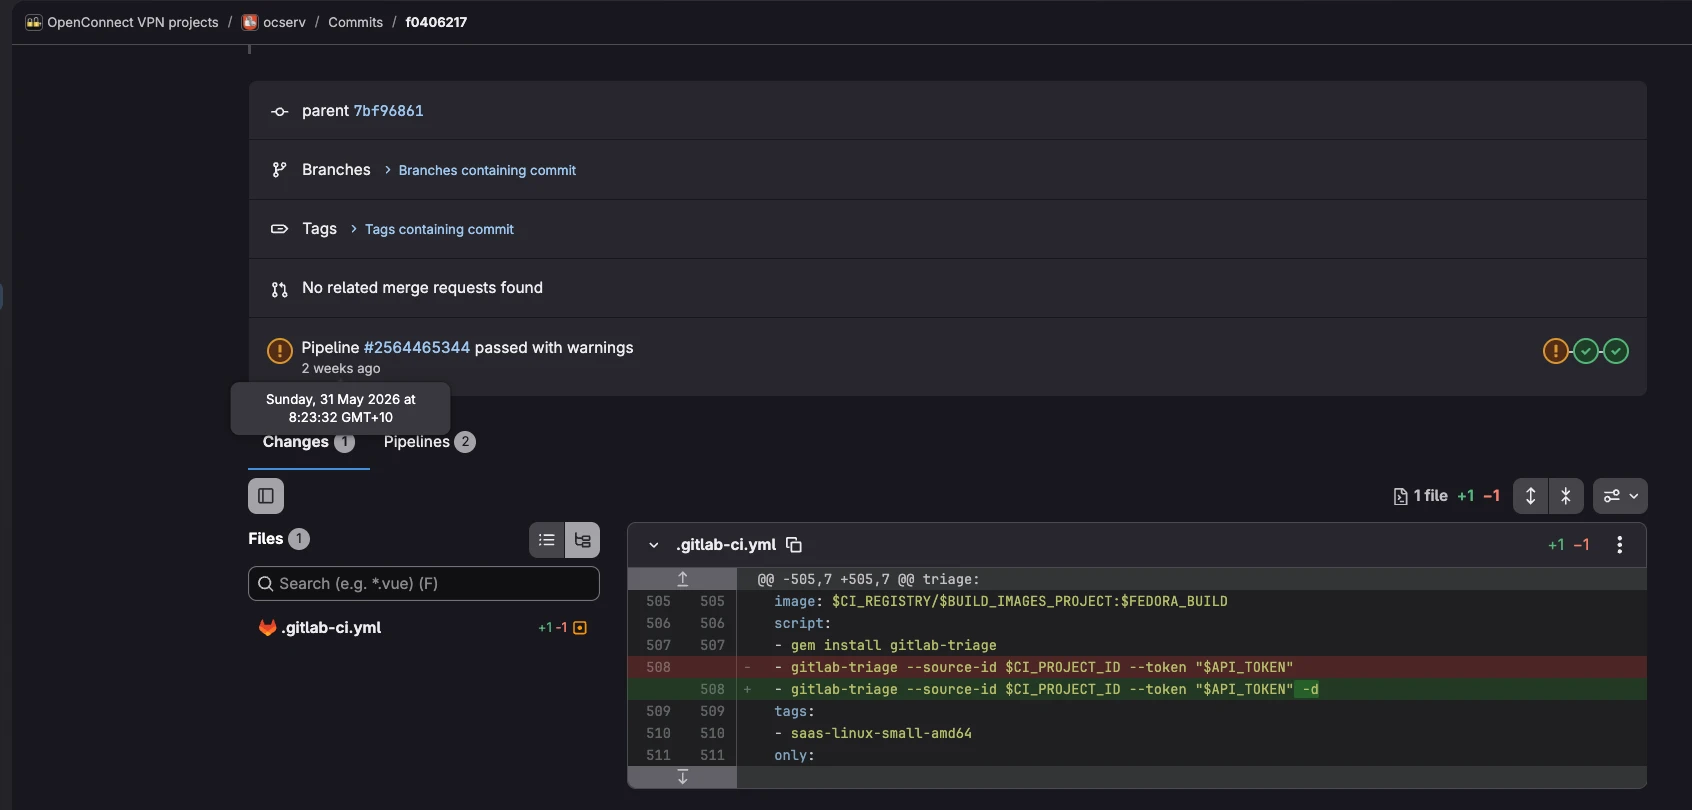
-
Check Point Patches Critical VPN Flaws Enabling Remote Code Execution
Check Point has issued emergency security updates on 9 September 2026 to fix two critical VPN flaws in the Quantum Security Gateway line. The vulnerabilities, CVE-2026-85102 and CVE-2026-85103, are rated CVSS v3.1 at 9.8 (Critical) and could allow…
-
SpyCloud Report Finds Non-Human Identities Lead Enterprise Attacks
SpyCloud has released its 2026 Identity Threat Report, which finds that non-human identities (NHIs) — including AI agents, service accounts, API keys and authentication tokens — are now the leading route into the modern enterprise. In the survey of 750…
SecurityOnline
-
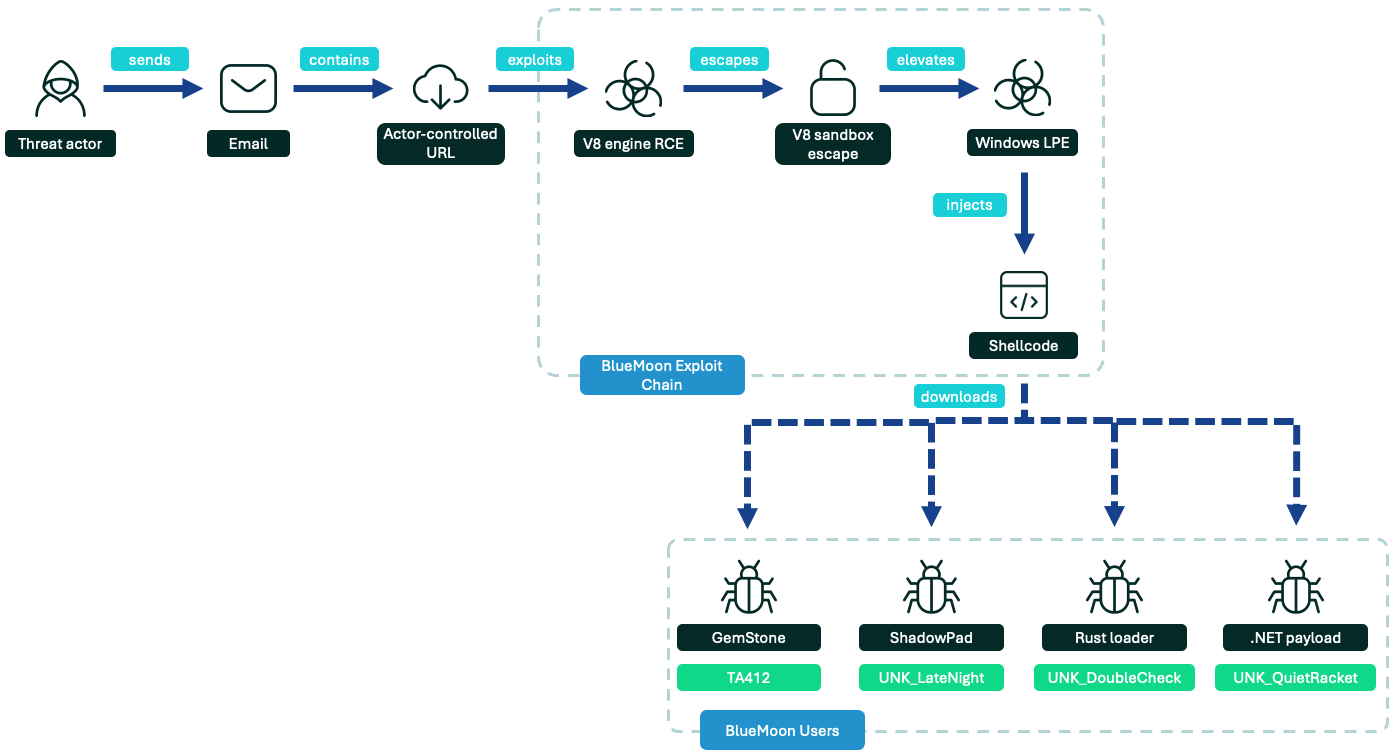
Chinese-Linked Spies Exploit Chrome and Windows Zero-Days
Proofpoint threat researchers have tracked a new BlueMoon exploit kit used in espionage campaigns, chaining Chrome/Chromium browser flaws with a Windows kernel privilege escalation to breach targeted networks. The operation, active from late August into…
-
Google Overhauls EU Search Results to Meet DMA Self-Preference Rules
Google has announced a major overhaul of its European search results in response to regulatory pressure under the European Union’s Digital Markets Act (DMA). The move follows a summer where the EU fined Google a total of 890 million euros, with 460 million…
SecurityOnline
-
Cisco UCS Servers Face Secure Boot Bypass via Public Exploit
Cisco has disclosed a high-severity vulnerability affecting its Unified Computing System (UCS) platform that enables a Secure Boot bypass via the UEFI shell. The flaw, tracked as CVE-2026-20293 with a CVSS v3 score of 7.1, could allow an authenticated user…
-
Google Fixes Critical Android Flaws Enabling Remote Code Execution
Google’s September 2026 Android security bulletin fixes a set of critical flaws across System, Framework and Kernel components, addressing remote code execution and privilege escalation risks. The bulletin confirms five CVEs in total, with one…
-
Meta launches Muse AI agent to automate shopping, travel and more
Meta has formally launched Muse, its end-to-end personal AI agent designed to act autonomously on a user’s behalf. Unlike prior conversational bots, Muse comes with its own dedicated app and web interface and operates without requiring technical know‑how.…
SecurityOnline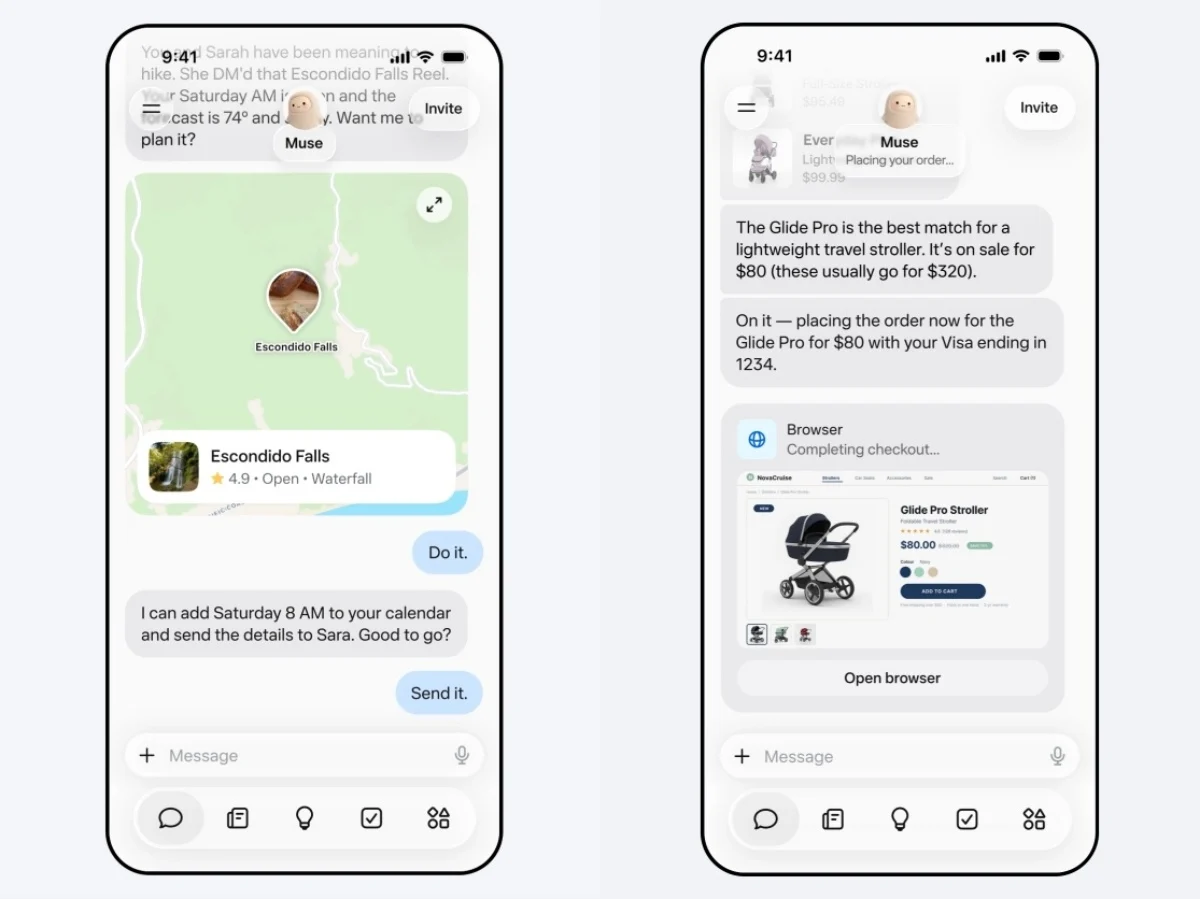
-
Fake macOS Installers Hide OtterCookie Backdoor in North Korean Campaign
Security researchers have identified a campaign in which fake macOS installers masquerade as legitimate utilities to deliver a backdoor known as OtterCookie. The attackers have trojanised disk images (DMG) and installer packages (PKG) that impersonate apps…
SecurityOnlineContagious Interview
-
Microsoft Bets on Local AI to Deliver ‘Unmetered Intelligence’ in Windows 11
Microsoft used the IFA 2026 event to push its vision of “unmetered intelligence” for Windows 11, reviving Bill Gates’ desk‑top promise with a heavy emphasis on local AI processing. The company says frontier AI models will still need substantial cloud…
SecurityOnline
-
OpenAI’s Images 2.5 Speeds Up Generation and Sharpens Editing
OpenAI has unveiled Images 2.5, the latest iteration of its image-generation model, promising better image detail, more precise editing, improved reference-photo consistency, and faster generation. The firm states that ChatGPT Images and the GPT-Image family…
SecurityOnline
-
Microsoft 365 Flaw Lets Spoofed Internal Emails Bypass Protection
Researchers have identified an active bypass of Microsoft 365’s RejectDirectSend control that enables spoofed internal emails to reach recipients. The flaw uses an empty SMTP envelope sender, allowing external senders to deliver unauthenticated messages that…
SecurityOnline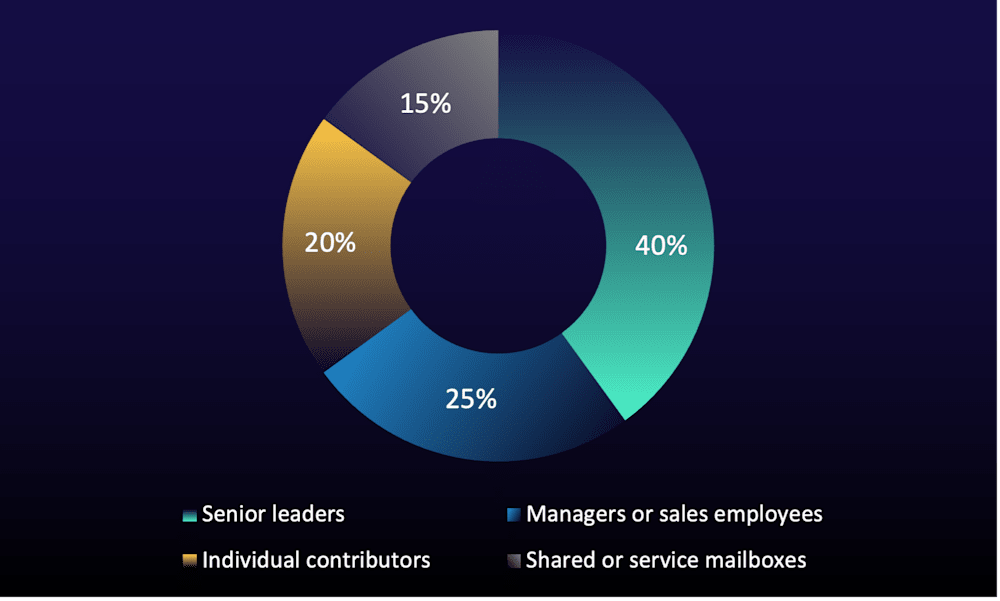
-
Windows 11 Previews Tease Automatic Theme Switching at Sunset
Windows 11 preview builds are teasing a long-awaited improvement: automatic light and dark theme switching. The article notes that hidden strings in the latest Windows 11 test builds describe a feature to alternate between light and dark modes, with the…
SecurityOnline
-
Apache Impala Flaws Let Attackers Seize Analytics Clusters Remotely
Apache Impala has four high-severity vulnerabilities that could let attackers take remote control of large analytics clusters. The flaws include an authentication bypass and remote code execution, along with server-side request forgery (SSRF) issues. The…
-
Asahi Linux Brings Apple M3 Support to Kernel 7.2, With Major Gaps
Asahi Linux has announced progress in bringing support for Apple’s M3-series chips, with the first M3 platform code now merged upstream in Linux kernel 7.2. After extensive reverse engineering, developers report that many functions already present on M1 and…
SecurityOnline
-
Critical Predis Flaw Lets Attackers Smuggle Commands into Redis
Security researchers have disclosed a critical vulnerability in the Predis PHP client for Redis, tracked as CVE-2026-84372. The flaw, rated CVSS 9.8 (Critical), has public PoC exploit code and is tied to a CRLF (carriage return line feed) sequence in the…
-
Critical MapLibre Flaw Enables Zero-Click XSS in Map Apps
MapLibre GL JS has a critical XSS flaw, CVE-2026-85061, affecting applications that render untrusted map styles or custom attributions. The vulnerability sits in the library prior to version 6.4.1 and is described as a sanitizer bypass in DOM[.]sanitize()…
-
Google Doubles Chrome Release Speed With New Biweekly Updates
Google has announced a shift to a two‑week release cadence for Chrome, beginning with Chrome 153 released on 9 September 2026 across Windows, macOS, Android and iOS. The move shortens the previous four‑week cycle introduced in 2021 to a biweekly pattern,…
SecurityOnline
-
cPanel SQL Flaw Lets Privileged Accounts Seize Servers with Root Access
CVE-2026-67401 is a newly disclosed SQL injection flaw in cPanel that could allow an attacker to gain full control of a server. The advisory describes an authenticated cPanel account holder with mail-related privileges who can abuse cPanel’s Email Track…
-
3,562 Exposed Redis Servers Hijacked in Rogue Replication Attack
Researchers from Hunt[.]io uncovered a Redis-based cryptomining operation that compromised 3,562 internet-facing Redis servers, largely on APAC cloud hosts. The attacker used a rogue replication method to point victims at a fake Redis master, delivering a…
SecurityOnline
-
CVE-2026-41870: Unauthenticated RCE in Apache Nutch
The page reports on four critical vulnerabilities detected in various software. Key points include: 1. **CVE-2026-75650**: An Adobe Commerce and Magento vulnerability concerning improper neutralization of special template elements. 2. **CVE-2026-81963**: A…
-
Siemens Flaws Let Attackers Hijack Accounts and Gain Root Access
Siemens ProductCERT disclosed two critical vulnerabilities affecting Industrial Edge and Siveillance Open Interface Services (OIS) on 8 September 2026. The flaws carry CVSS scores above 9.0. The first, CVE-2026-18963, resides in the password reset flow of…
-
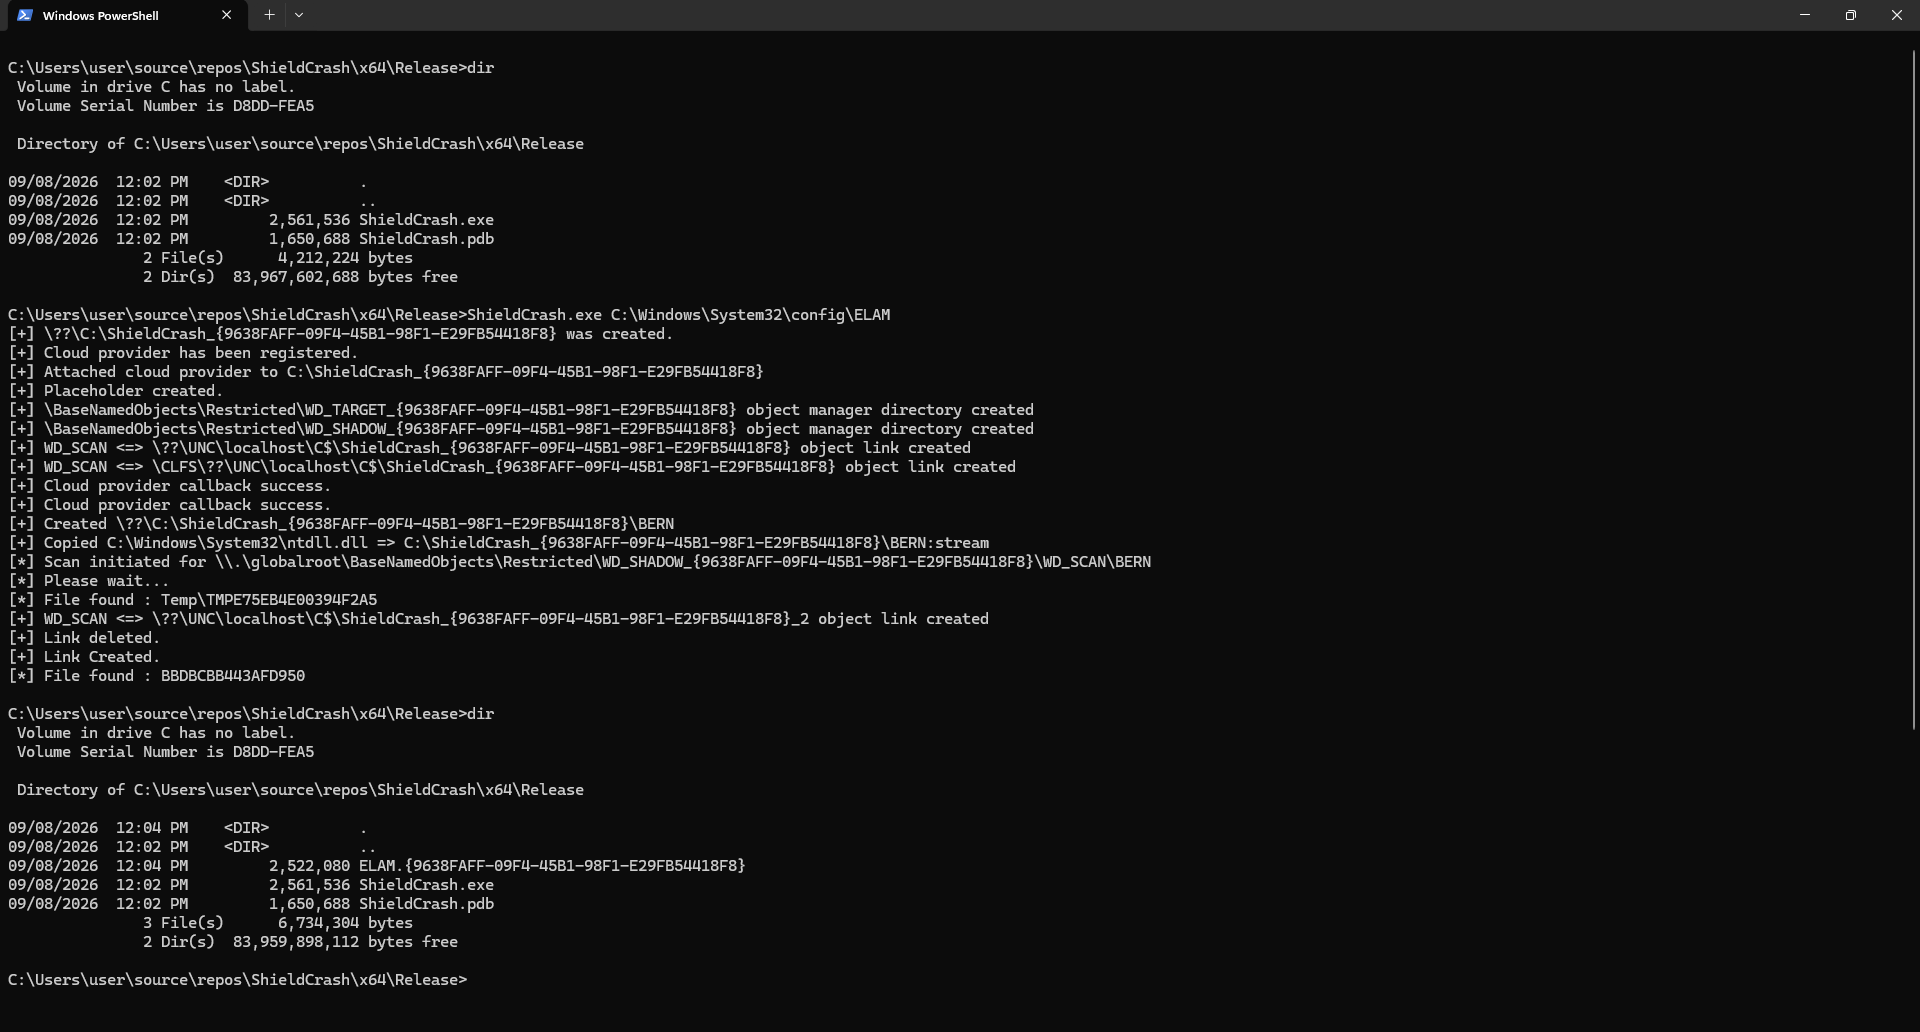
Microsoft Defender 0day PoC Exposes SYSTEM Files on Windows
A publicly available 0day in Microsoft Defender, dubbed ShieldCrash, has been disclosed with a working PoC that can read arbitrary files as SYSTEM on all supported Windows versions. The flaw is associated with CVE-2026-69414 and follows an initial…
-
Critical Hawtio Operator Flaw Enables Cross Tenant Impersonation and RCE
Red Hat has flagged a critical vulnerability in Hawtio Operator used with Kubernetes and OpenShift. Identified as CVE-2026-78234 and rated CVSS 9.9, the flaw affects Hawtio-operator installations that rely on the OpenShift Service CA for client…
-
Chrome 153 Patches Exploited V8 Zero Day and 229 Flaws
Google has released Chrome 153 to address 230 security flaws, including a zero-day vulnerability in the V8 JavaScript engine that is already being exploited in the wild. The flaw, CVE-2026-87491, is described as an out-of-bounds write in V8 that could allow…
-
AI-Assisted Attacks Target Latin American Transport and Banks
Palo Alto Networks Unit 42 reports two AI-assisted intrusion campaigns targeting Latin American organisations, with activity spanning Mexico, Ecuador and Brazil. In both cases, attackers leveraged commercial large language models to script or enhance…
SecurityOnline