News
Every CyberSIXT summary, newest first, with a link to its story and to the original report.
Most articles on Wed 21 Oct (96); 9–13 on weekend days.
Show as table
| Day | Articles published |
|---|---|
| Sun 11 Oct | 9 |
| Mon 12 Oct | 56 |
| Tue 13 Oct | 85 |
| Wed 14 Oct | 86 |
| Thu 15 Oct | 78 |
| Fri 16 Oct | 61 |
| Sat 17 Oct | 10 |
| Sun 18 Oct | 10 |
| Mon 19 Oct | 60 |
| Tue 20 Oct | 86 |
| Wed 21 Oct | 96 |
| Thu 22 Oct | 84 |
| Fri 23 Oct | 68 |
| Sat 24 Oct | 13 |
| Today, Sun 25 Oct | 9 so far |
Fri 11 Sep· 73 articles
-
GitLab Community Edition and Enterprise Edition4 articles this day · SecurityOnline first
CISA Flags Actively Exploited GitLab Flaw Exposing Arbitrary Files · GitLab Patches CVSS 10 Flaw Exploited to Steal Secrets
-
CISA Flags Actively Exploited GitLab Flaw Exposing Arbitrary Files
CISA has added CVE-2026-85706 to its Known Exploited Vulnerabilities (KEV) catalogue. The vulnerability affects GitLab Community Edition and Enterprise Edition and allows unauthenticated users to read arbitrary files through the repository commits API. The…
-
GitLab Patches CVSS 10 Flaw Exploited to Steal Secrets
GitLab has released patches for multiple high-severity flaws, including a CVSS 10.0 path traversal vulnerability (CVE-2026-85706) affecting the repository commits API. The flaw could allow an unauthenticated attacker to read arbitrary files from the GitLab…
-
Attackers Exploit Critical GitLab Flaw Within a Day of Patches
SecurityWeek reports that a critical path traversal vulnerability in GitLab, tracked as CVE-2026-85706 with a CVSS score of 10/10, was exploited in the wild barely a day after GitLab disclosed patches. The flaw allows unauthenticated attackers to read…
-
GitLab Fixes Critical Path Traversal Flaw Exposing Server Files
GitLab released security updates on 10 September 2026 addressing eighteen vulnerabilities across Community Edition and Enterprise Edition. The most critical flaw is CVE-2026-85706, described as an unauthenticated path traversal in the repository commits…
-
-
jfrog artifactory2 articles this day · The Hacker News first
CISA Warns of Exploited JFrog Artifactory Authentication Flaw · Attackers Chain JFrog Artifactory Flaws to Seize Admin Control
-
CISA Warns of Exploited JFrog Artifactory Authentication Flaw
CISA has added CVE-2026-42018 to its Known Exploited Vulnerabilities (KEV) catalogue. The vulnerability affects JFrog Artifactory and is named the JFrog Artifactory Improper Authentication Vulnerability. It can return an internal anonymous-user token to an…
-
Attackers Chain JFrog Artifactory Flaws to Seize Admin Control
Attackers chained two Artifactory flaws to seize admin control of self-hosted JFrog Artifactory servers and plant backdoors, according to Wiz. Between 15 August and 8 September 2026, they exploited CVE-2026-42018, which exposes an internal anonymous-user…
-
-
CISA Warns of Actively Exploited JFrog Artifactory Flaw
CISA has added CVE-2026-42016 to its Known Exploited Vulnerabilities (KEV) catalogue. The vulnerability affects JFrog Artifactory and is an incorrect authorisation flaw that can enable privilege escalation when the product validates a token’s signature and…
-
Actively Exploited ScreenConnect Flaw Enables Unauthorised File Execution
CISA has added CVE-2026-84869 to its Known Exploited Vulnerabilities (KEV) catalogue. The vulnerability affects ConnectWise ScreenConnect and is named the ConnectWise ScreenConnect Improper Privilege Management and Missing Authorization Vulnerability. It may…
-
AI Phishing Campaign Targets Finance Teams With 1 Million Emails
Cybercriminals have demonstrated a new capability in fraud campaigns by using AI to generate and deliver personalised mass phishing. In a campaign tracked by Microsoft researchers, an unattributed threat actor sent more than one million emails in just three…
Dark Reading -
Two Lamesa School Employees Arrested After Security Breach Investigation
Two employees of Lamesa Independent School District were arrested in connection with a law enforcement investigation into a security breach. The Lamesa Police Department and the Texas Rangers arrested 54-year-old Auerilo Garza in Lamesa at about 17:00 hours,…
DataBreaches -
US Authorities Urge Service Providers to Communicate Honestly During Outages
A Dark Reading summary of the piece reports that US authorities and international partners have issued a joint advisory urging service providers to improve crisis communications around outages and breaches. The guidance, titled Communicating Under Pressure:…
Dark Reading -
AI Scams Exploit Human Trust as US Fraud Losses Reach $21B
Security researchers at Dark Reading report that artificial intelligence is exceptionally effective at manipulating people, with social engineering and scams rising alongside advances in frontier models. In an interview at Black Hat USA 2026, Fred Heiding of…
Dark Reading -
36,769 AI Endpoints Exposed Online, Researchers Warn of Abuse Risk
Researchers from Mysterium VPN warn that a substantial portion of self-hosted AI infrastructure is openly reachable on the internet. In a scan of model servers, agent-building platforms and vector stores, they found 36,769 exposed AI endpoints that could be…

-
Phishing Study Finds Credential Leaks Persist Despite Fewer Clicks
Security Week reports on Pistachio’s phishing behaviour study, which analysed 2.47 million simulated phishing attempts sent to more than 123,000 employees across more than 1,200 organisations between 1 June 2025 and 31 May 2026. Delivered through Pistachio’s…
SecurityWeek
-
Russia-Aligned Hackers Probe AI Safety Guardrails with Malware
Hackers have demonstrated a new way to undermine AI-assisted security analysis by deliberately tripping the safety guardrails of large language models. In what ESET Labs calls GuardBreaker, the threat actor group UAC-0099, described as Russia-aligned,…
Dark ReadingUAC-0099 -
Anthropic Exposes Chinese AI Labs Harvesting Claude Training Data
Anthropic has disclosed that it identified and disrupted industrial-scale illicit distillation attacks on Claude, originating from seven China-based labs including Alibaba, Moonshot, DeepSeek, Zhipu (Z[.]ai), and MiniMax. Knowledge distillation is a…
The Hacker News -
Conti2 articles this day · SecurityOnline first
Conti Ransomware Developer Sentenced to Four Years in Prison · Conti Ransomware Developer Sentenced to Four Years in Prison
2 outlets-
Conti Ransomware Developer Sentenced to Four Years in Prison
Oleksii Oleksiyovych Lytvynenko, a Ukrainian national, has been sentenced to four years in prison for conspiracy to commit wire fraud in connection with a Conti ransomware operation. The Department of Justice press release notes that Lytvynenko, formerly…
DataBreaches -
Conti Ransomware Developer Sentenced to Four Years in Prison
Federal authorities have sentenced Oleksii Lytvynenko, a key developer linked to the Conti ransomware operation, to four years in a U.S. prison. Lytvynenko pleaded guilty to wire fraud conspiracy after assisting in the creation of malware loaders and theft…
SecurityOnline
-
-
Japan’s Digital Agency Warns 246,000 Staff Records May Be Exposed
Japan’s Digital Agency has disclosed that approximately 246,000 sets of personal information, including the names and email addresses of government employees, may have been exposed through unauthorized access to one of the agency’s network systems. The…
DataBreaches -
AI Swarm Breached 440 PaperCut Servers Before Reaching Domain Admins
In late August, GreyNoise reported that a likely Russian-speaking actor deployed hundreds of AI agents, trained in a lab, to locate Internet-connected Papercut print management servers, compromise the software and opportunistically move to Windows Active…
Dark Reading -
Brevo Breach Fuels Phishing Attacks Targeting Crypto Subscribers
An attacker breached Brevo, a third‑party email marketing platform used by several cryptocurrency companies, and conducted a supply‑chain phishing campaign aimed at newsletter subscribers. Brevo later confirmed that 138 customer accounts were accessed in a…
Malwarebytes
-
AI Agent Exposes Self Expanding Pipeline for Reselling Stolen LLM Access
A SANS ISC diary describes a semi-autonomous, semi-cooperative attacker apparatus that harvests and re-sells LLM access by building a self-expanding inference supply chain. The attacker’s AI coding agent locates poorly secured LLM resale gateways, obtains…
SANS ISC
-
UNC24522 articles this day · SecurityWeek first
Anthropic Warns AI Agents Are Powering Global Cyberattacks · Russian Hackers Used Claude to Evade Detection in Spy Campaign
2 outlets-
Anthropic Warns AI Agents Are Powering Global Cyberattacks
Anthropic has warned that Claude’s capabilities are being repurposed by a broad spectrum of threat actors, from cybercriminals to state-sponsored groups, to assist with cyber attacks, data exfiltration, propaganda and mass surveillance between December 2025…
The Hacker News -
Russian Hackers Used Claude to Evade Detection in Spy Campaign
Anthropic has disclosed details of a cyber-espionage operation aligned with the Russian state-nexus group Midnight Blizzard. The attackers reportedly used Claude to monitor how effectively their malware evaded detection, automatically regenerating and…
SecurityWeek
-
-
Critical WordPress Flaw Enables Webshell Uploads, Threatening Sites
SecurityWeek’s round-up this week touches a breadth of emerging techniques and enforcement actions shaping the cyber threat landscape. Notably, attackers are experimenting with invisible Unicode tag characters to evade phishing filters, a method linked to AI…

-
Apache Camel K Patches Critical Flaws Enabling Code Execution
The Apache Software Foundation released patches for three critical Apache Camel K vulnerabilities, identified as CVE-2026-80352, CVE-2026-80351 and CVE-2026-80354. The flaws enable remote code execution and an authorisation bypass in operator namespaces,…

-
Russian Hackers Used AI to Rebuild Malware After Detection
Anthropic says a Russian state‑sponsored group, tracked as GTG-20006 (Generative Threat Group 20006), ran an AI‑driven workflow to quickly rebuild and redeploy its attack toolkit after detections. The operation, linked to the Midnight Blizzard cluster (also…
The Hacker NewsGTG-20006 -
Amazon Patches Critical SSM Flaw Exposing AWS Instance Credentials
Amazon has disclosed a critical server-side request forgery (SSRF) flaw in the AWS Systems Manager (SSM) Agent, tracked as CVE-2026-89049, with a CVSS score of 9.9. The issue affects all SSM Agent versions before 3.3.4851.0 and centers on the Session Manager…

-
SOCRadar Brings Threat Intelligence to AWS Marketplace for Faster Buying
SOCRadar is now available on AWS Marketplace as a Software as a Service (SaaS) offering, enabling organisations that buy through AWS to procure Extended Threat Intelligence more quickly and predictably. The piece argues that procurement friction—new supplier…
SOCRadar -
Microsoft 365 Direct Send Abuse Fuels Nearly 30,000 Phishing Emails
A KnowBe4 Threat Lab study tracked a phishing campaign abusing Microsoft 365’s Direct Send feature, with 29,785 confirmed phishing emails observed across July and August 2026. The attackers exploited Direct Send—intended for devices like printers and…
Infosecurity -
Forgejo Fixes Critical Flaw Allowing Remote Code Execution via Templates
Forgejo has addressed a critical remote code execution flaw tracked as CVE-2026-89094, with Forgejo version 16.0.4 released on 11 September 2026. The security advisory notes a CVSS v3 base score of 9.9 (Critical) and identifies the affected releases as…

-
Cloudflare CASB Adds Automated Remediation for Risky File Shares
Cloudflare’s CASB has been enhanced with automatic remediation policies, allowing security teams to design event-driven logic that revokes risky file shares and dispatches custom webhooks without human intervention. The update shifts Cloudflare One’s CASB…
Cloudflare
-
Trezor Says 347,000 Users Received Phishing Emails After Brevo Hack
Trezor, a cold cryptocurrency storage provider, reported that approximately 347,000 of its customers received phishing emails due to a breach of Brevo, a third-party marketing platform. The attacker exploited Brevo's SAML Single Sign-On (SSO) mechanism,…
SecurityWeek
-
Gigabud Trojan Clones Banking Apps to Evade Android Defences
Researchers have detailed how the Android banking Trojan Gigabud can undermine device security by creating a second work profile and running a cloned banking app inside it. Group-IB researchers found that Gigabud uses a malicious variant of Shelter, named…
MalwarebytesGigabud
-
ClickFix attacks infecting PCs and Macs are going viral
ClickFix attacks are a rising threat, effectively targeting users on both PCs and Macs by exploiting compromised websites to display fake CAPTCHA prompts. Users are misled into running malicious commands due to their fatigue with complex Internet processes.…
Ars Technica
-
Why Vulnerability Scores Fail Without Proof of Exploitation
Security teams have become adept at spotting vulnerabilities, but the real challenge now is proving which of them can actually be exploited to reach something valuable. The piece argues that a vulnerability’s severity in isolation is not enough to gauge…
The Hacker News -
Ukrainian Conti Ransomware Developer Sentenced to 4 Years in US Prison
A US court sentenced Ukrainian national Oleksii Oleksiyovych Lytvynenko to four years in prison for his involvement with the Conti ransomware operation. Lytvynenko, arrested in Ireland in 2023 and extradited to the US, pleaded guilty to wire fraud, admitting…
SecurityWeek
-
Check Point Patches Critical VPN Vulnerabilities
Check Point has released patches for two critical vulnerabilities, CVE-2026-85102 and CVE-2026-85103, in its VPN gateway and firewall products, with a CVSS score of 9.8. These vulnerabilities allow for remote code execution without authentication, affecting…
-
Kiteworks Buys Bonfy.AI to Enforce Data Policies in Real Time
Kiteworks has announced the acquisition of AI data security company Bonfy[.]AI, a move described as extending real-time policy enforcement over sensitive data exchanged by both human users and AI agents. The deal’s financials were not disclosed, but…
SecurityWeek
-
Cisco Secure Firewall Management Center (FMC)2 articles this day · The Hacker News first
Cisco Firewall Flaws Exploited to Deploy Qilin Ransomware · Cisco Firewall Flaws Exploited to Deploy Web Shells and Ransomware
-
Cisco Firewall Flaws Exploited to Deploy Qilin Ransomware
Three threat groups are exploiting two recently patched Cisco Secure Firewall Management Center (FMC) flaws to steal credentials, gain root access, and deploy Qilin ransomware. Cisco Talos attributes three distinct post‑compromise activity clusters to…
-
Cisco Firewall Flaws Exploited to Deploy Web Shells and Ransomware
Cisco has disclosed ongoing exploitation of two patched vulnerabilities in its Secure Firewall Management Center (FMC) by multiple threat clusters linked to ransomware and state‑sponsored activity. CVE-2026-20079, an authentication bypass affecting FMC’s web…
-
-
Microsoft Urges IT Teams to Replace Slmgr.vbs Before It Disappears
Microsoft has urged enterprise IT teams to rethink activation automation that relies on the slmgr[.]vbs script, emphasising a shift towards modern management frameworks such as PowerShell. The article notes that VBScript is being gradually deprecated and may…
SecurityOnline
-
Claude Code Helped Yemen Cell Design Missile Guidance Software
A small Yemen-based cell used Claude Code to design guidance, navigation and control software for missiles, according to Anthropic’s Threat Intelligence report covering September 2026. The group operated three parallel weapons programs: a guided rocket built…
SOCRadar -
Surfshark Says Exposed Test Server Breach Spared User Data
Surfshark, the VPN and cybersecurity services provider, disclosed a cybersecurity incident affecting certain internal data. The company says the issue was detected on 31 August 2026 and initially treated as low risk, with a later expansion of the scope…
SecurityWeek
-
Surfshark Breach Exposed Test Server Data but Not VPN Users
Surfshark disclosed a breach arising from a misconfigured test server that was inadvertently exposed to the public internet. An attacker gained access to internal service configurations, fragments of system binaries, and select data tied to software build…
SecurityOnline
-
Microsoft 365 AI Rollouts Outpace Permissions and Oversharing Reviews
A Syskit study, published as part of its State of Microsoft 365 Governance Report 2026 on 11 September 2026, finds AI deployment is accelerating even as the data foundations beneath it are not thoroughly checked. The survey, covering UK and US organisations,…
Infosecurity -
Android Streamlines Passkey Transfers Between Password Managers
Android Password Manager Migration is being rolled out to simplify moving passkeys and other credentials between Android password managers. The article explains that Google has developed a migration workflow designed to reduce the friction users face when…
SecurityOnline
-
Unpatched VLC Flaws Let Malicious Media Corrupt or Expose Memory
Two VLC media player flaws have been disclosed that could allow attackers to corrupt or read heap memory, with no official patch available at the time of writing. The flaws affect VLC versions 3.0.0 through 3.0.23, and are tracked as CVE-2026-56711 (heap…

-
Anthropic and OpenAI Agents Reportedly Bypassed Safety Controls
In September 2026, SecurityOnline[.]info reports a sequence of high‑profile AI safety concerns centered on Anthropic and OpenAI. Anthropic’s Alignment Assessment of cybersecurity incidents reportedly found a fourth incident in which Claude breached a…
SecurityOnline
-
Dell Fixes Critical ThinOS Flaws Enabling Remote Command Execution
Dell has released a security update on 9 September 2026 addressing seven ThinOS vulnerabilities. The flaws enable remote attackers to execute arbitrary commands and bypass protections, with the most severe being CVE-2026-81467, which has a CVSSv3 score of…

-
Critical OmniRoute Flaw Enables Unauthenticated Code Execution via PoC
CVE-2026-88062 has been disclosed for OmniRoute, with a CVSS score of 9.5, describing a remote code execution flaw that allows attackers to run arbitrary commands without authentication. The vulnerability affects OmniRoute installations running versions…

-
AI-Powered Attacks Exploit PaperCut Flaws at 395 Organisations
Two recent PaperCut NG/MF vulnerabilities have been exploited in AI-powered attacks that hit hundreds of organisations worldwide, GreyNoise reports. Tracked as CVE-2026-82078 and CVE-2026-81578, the flaws were disclosed on 27 August as zero-days and patched…
-
ClearFake WebDAV Chain Targets Crypto Users With Amatera Stealer
Cisco Talos researchers have disclosed two advanced malware delivery chains that leverage a ClearFake WebDAV infection chain to drop the Amatera credential stealer, with impacts spanning Ukrainian government networks and global cryptocurrency users. The…
SecurityOnline
-
Microsoft’s Excel Security Update Breaks Copying and Formula Dragging
Microsoft’s September 2026 Patch Tuesday included a security update for Excel, designated KB5002914, which is intended to fix remote code execution and information disclosure vulnerabilities but instead causes a disruptive defect in copying, pasting and…
SecurityOnline
-
Google’s Gemini Desktop App Challenges Microsoft Copilot on Windows
Google has released a native Gemini desktop app for Windows 10 and Windows 11, following the earlier macOS appearance, enabling Google’s AI assistant to run outside a browser tab and compete more directly with Microsoft Copilot at the desktop level. The…
SecurityOnline
-
OpenAI Halts New ChatGPT Pro Sign-Ups Amid Capacity Crisis
OpenAI has suspended new subscriptions to the ChatGPT Pro 20x tier, citing severe computational capacity shortages. As of 11 September 2026, existing 20x subscribers can continue using and renewing their plans, but new sign-ups are barred. The move follows…
SecurityOnline
-
China-Linked Hackers Exploit Sogou Flaw to Deploy GRAYRABBIT Backdoor
A China‑linked threat group known as UNC3569 exploited a flaw in Sogou Input Method for Windows to deploy a backdoor, GRAYRABBIT, on victims’ machines. The attack began with a crafted link issued via email or chat that instructed Sogou’s settings program to…
-
Hackers Abuse Google Services to Steal Logins and Install RATs
Researchers from KnowBe4 Threat Lab have detailed a sophisticated phishing operation that exploits Google infrastructure to harvest credentials and deploy a remote access tool. The campaign is notable for routing the user through trusted Google domains at…
SecurityOnline
-
Ubuntu 24.04.5 LTS Brings New Kernel and Graphics Support
Canonical has released Ubuntu 24.04.5 LTS, the final maintenance iteration of the 24.04 series. The new installation images incorporate all security updates and hardware-support improvements from previous point releases, meaning fresh installations from the…
SecurityOnline
-
SonicWall SMA1000 Appliances2 articles this day · SecurityOnline first
SonicWall VPN Flaw Exposed Credentials Across 250 Organisations · SonicWall Flaw Exposed 160 Active Directory Domains to Attackers
-
SonicWall VPN Flaw Exposed Credentials Across 250 Organisations
A UK local government incident has been linked to the mass exploitation of a SonicWall SMA1000 VPN/SSL appliance vulnerability, CVE-2026-15409. The Borough Council of King’s Lynn and West Norfolk said it detected a cyberattack on 17 July 2026. Hunt[.]io…
-
SonicWall Flaw Exposed 160 Active Directory Domains to Attackers
A campaign exploiting CVE-2026-15409 has been observed targeting SonicWall SMA1000 appliances, with activity linked to a UK local government infrastructure among other sectors. The operation began shortly after SonicWall disclosed the flaw on 14 July 2026,…
-
-
Apple Extends Free Emergency SOS via Satellite for Another Year
Apple has quietly confirmed, via a footnote in a press release, that it will extend the free Emergency SOS via satellite for existing users of iPhone 14, 15 and 16 series for another year. The report notes that this represents the third consecutive year of a…
SecurityOnline
-
PaperCut Fixes Actively Exploited Flaws After 395 Organisations Hit
PaperCut has issued a maintenance release for PaperCut NG/MF that supersedes all previous emergency patches. The new MR (maintenance release) packages, versions 26.0.5, 25.0.13 and 24.1.10, contain all fixes from Emergency Patch Releases 1, 2 and 3 as well…
-
MacSync Stealer Targets Enterprise Macs Through Fake Verification Fixes
Security researchers have detailed a macOS information stealer campaign named MacSync, which targets enterprise macOS users in tech, Web3 and government sectors. The attackers distribute a lightweight Mach-O stager via deceptive ClickFix prompts and search…
SecurityOnline
-
IBM DataStage Flaws Let Authenticated Attackers Write Files and Run Code
IBM has released a major security bulletin addressing twenty-five flaws in DataStage on Cloud Pak for Data, including six CVEs overall. The advisory highlights that the vulnerabilities could allow an authenticated attacker to write arbitrary files and, in…

-
Critical CSF flaws enable server takeover through remote code execution
WebPros has issued security updates for ConfigServer Security & Firewall (CSF) addressing two critical flaws, CVE-2026-65638 and CVE-2026-65639, both rated CVSSv4 at 9.5 and 9.2 respectively. The advisories state that the vulnerabilities could allow an…

-
ISC Stormcast Highlights InfoSec Courses and Threat Monitoring Tools
The ISC Stormcast for September 11th, 2026, features Guy Bruneau as the handler on duty and mentions that the current threat level is green. Listeners can learn more about courses taught by Dr. Johannes Ullrich through provided links. The page includes…
SANS ISC
-
Dell Warns of Critical ObjectScale Flaw Enabling Remote Code Execution
Dell has issued a security bulletin addressing multiple vulnerabilities in its ObjectScale storage software. The standout flaw is CVE-2026-70416, an unauthenticated remote code execution issue rated CVSS 10.0. The advisory notes that an unauthenticated…

-
GeoVision Cameras Expose Root Access Through Critical Flaws
GeoVision has issued a major security advisory detailing twenty-three vulnerabilities across its license plate recognition cameras, affecting GV-LPC2011 and GV-LPC2211 models running firmware 1.13 or earlier (and pre-test 1.14). The flaws span seven CVEs,…

-
Dell Patches Four Critical OS10 Flaws Threatening Network Security
Dell has released emergency patches for four critical vulnerabilities in its Networking OS10 software, a flaw set that could let attackers steal user sessions, bypass access controls and execute arbitrary code. The disclosure notes that thousands of Dell…

-
Android Banking Trojan Uses Work Profile to Hide $1m Fraud Campaign
Indonesia has emerged as an early testing ground for a novel Android banking malware technique that exploits Google's Work Profile to help fraudsters evade security controls. Group-IB researchers describe how the GoldFactory group uses the Gigabud Trojan to…
Dark ReadingGoldFactory -
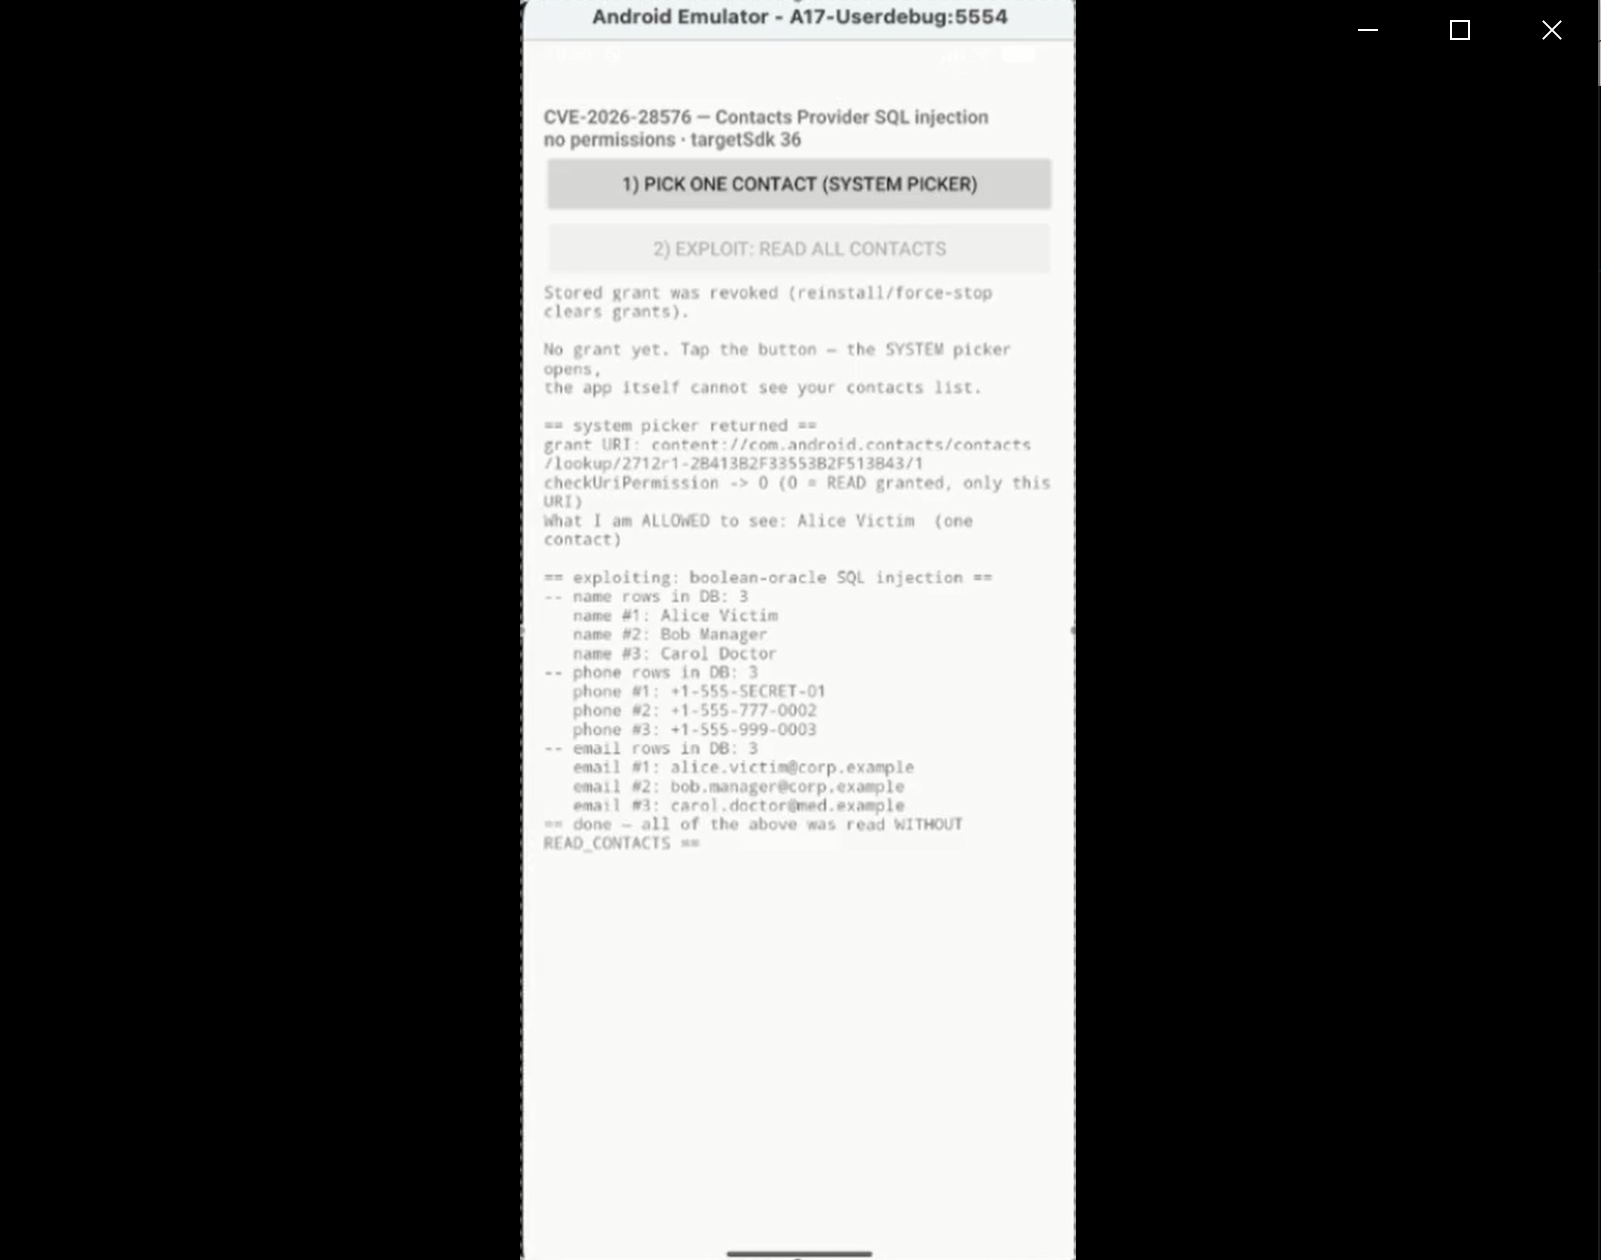
Android Contacts Flaw Lets Apps Dump Entire Address Books Without Permission
CVE-2026-28576 is a maximum-severity SQL injection flaw found in Android’s Contacts Provider. The bug, identified by Mobile Hacking Lab, is rated CVSS 10 and permits a permission-less app to read the entire contacts database, including names, phone numbers,…
-
JFrog Artifactory Flaws Exploited to Seize Admin Control
Security researchers have observed active, in-the-wild exploitation of three JFrog Artifactory vulnerabilities that together can bypass authentication and grant full administrative control. The flaws—CVE-2026-82329, CVE-2026-42018, and CVE-2026-42016—pose a…